The first fraud alert at Hailo did not arrive from a gleaming machine-learning console. It came from taxi drivers. Around 2012, drivers using the London ride-hailing app began saying that certain jobs felt wrong. Chargebacks followed. The app was scaling fast, the crooks were keeping pace, and fraud products designed for airlines or old-school retail did not understand an on-demand ride dispatched in seconds.
Martin Sweeney was brought into Hailo to work on the problem. With colleagues Nick Lally, Mairtin O’Riada, Leonard Austin and Stephen Whitworth, he found a gap large enough to become a company. On October 21, 2014, the five met at The Blackfriar pub, filled in the incorporation form and clicked submit. They called the new operation Ravelin, after the triangular defensive work outside a fortress wall. The logo is a star fort. Subtle it is not, but then neither is a stolen credit card.
The first thing to fail was the off-the-shelf answer
The founders’ insight was born on the buyer’s side. Hailo had looked for a vendor and found systems calibrated to slower, different businesses. A taxi app sees new accounts, moving locations, small baskets and immediate fulfillment. A model trained on a holiday booking made months ahead can be perfectly respectable and still be wrong for a ride across Soho at midnight.
Hailo became Ravelin’s first customer before there was a finished product. That trust changed the usual startup sequence. Sweeney has said the classic minimum viable product approach did not work for cybersecurity and payments: a charmingly incomplete beta is less charming when it approves theft or rejects a real passenger. The team built for safety first, commercially launched after paid trials in January 2016 and reported revenue growth of more than 600 percent in the next nine months.
One decision, four layers
A machine that knows your regulars
Ravelin’s core service ingests a merchant’s customer, order, payment and device events through APIs. Its models turn those events into a risk score and a recommended action. Rules remain available for firm business policies; humans can investigate in a dashboard; confirmed fraud and chargebacks flow back as labels. The useful distinction is that Ravelin trains models for individual merchants instead of pretending every shop has the same villains.
Connect, its graph product, supplies the detective board. It maps accounts linked by cards, devices, phone numbers, emails or IP addresses. One suspicious order may reveal 59 accounts orbiting the same device. Network traits also become model features, so a connection contributes to a score rather than acting as an automatic guilty verdict. Ravelin once noted that the graphs were pretty enough to frame for clients. This is data visualization with an unusual interior-design brief: lovely colors, terrible people.
The product followed fraud away from checkout. Ravelin now covers account registration and takeover, promotion and voucher misuse, refunds and returns, supplier and marketplace fraud, 3D Secure authentication and transaction optimization. In early 2026 it added labels and rule conditions for agentic commerce, giving merchants a way to distinguish a shopping bot from a human without assuming every automated visitor is hostile.
“If a new customer is erroneously prevented from buying, and then never comes back... this is the worst-case scenario for us.”Nick Aiken, Director of Fraud and Payments at Trainline
The business hidden inside “yes”
Security software is often sold with a fear gauge: attacks caught, losses blocked, bad actors banished. Ravelin also talks about approvals. A false positive is an honest buyer treated like a crook, and the bill includes the rejected sale, the embarrassed customer and whatever they would have bought next year. This is why payment fraud and payment optimization belong in the same product conversation.
Trainline decided in 2019 that its fraud operation should become machine-learning-first. Since working with Ravelin, the ticket platform says its block rate fell 75 percent in the UK and 64 percent in European markets, manual reviews dropped 92 percent and fraud stayed low. River Island offers the cleaner before-and-after picture. Its small team had maintained more than 300 active rules and covered reviews 16 hours a day, seven days a week. After moving to automated decisioning, it reported fewer than 40 rules, no manual review and more than 2,500 analyst hours released for other work.
Selected customer-reported change
Flix provides the other side of the equation. After Ravelin enriched its custom models with Mastercard identity data, the travel company reported a 40.7 percent uplift in acceptance. Dispute rates fell 14.9 percent at Flix and 19.3 percent at Greyhound. More good sales and fewer disputes is the combination buyers want; maximizing either measure alone is easy and commercially silly.
The buyers are fraud, risk and payments teams at online retailers, marketplaces, travel companies and digital-goods businesses. Named customers include Spotify, Deliveroo, Just Eat, Trainline, Tesco, John Lewis, Back Market and Nando’s. Ravelin sells enterprise SaaS directly and through payment partners. There is no public price card. Prospects book a demo, then buy a contract shaped by transaction volume, products and integration scope. Anyone seeking a £49-per-month toggle will leave disappointed.
A technical company with a dartboard
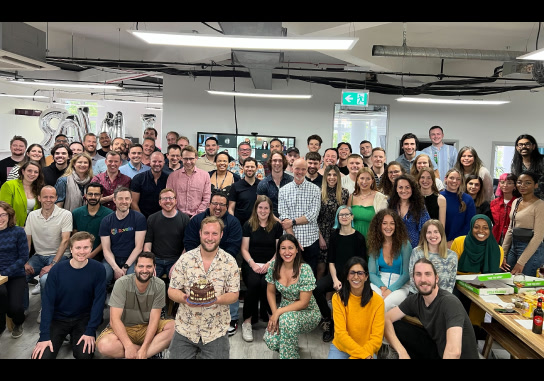
Ravelin says 85 percent of its staff work in technical teams, dominated by engineering and data science. Its stated values are integrity, ambition, resourcefulness and thoughtfulness. The careers pitch is remote-first and unusually specific about behavior: disagreement is welcome, disrespect is not. The company timeline also records installation of its first office dartboard beside the 2015 milestone of monitoring one million transactions. History needs texture.
The work is not model worship. Dedicated integration, product-support and data-science teams sit around the software. Analysts get a data warehouse, rules, case tools and graph investigations. That mixture is Ravelin’s answer to a black-box objection: show the signals behind a score, preserve room for policy and let fraud specialists challenge the machine. Machine learning takes repetitive judgment out of the queue; it does not repeal judgment.
Worldpay buys the decision layer
Venture investors financed the expansion. Disclosed rounds included £1.3 million in 2015, £3 million in 2016, £8 million in 2018 and £16.4 million in 2020. The last was led by Draper Esprit, now Molten Ventures, with Amadeus Capital Partners, BlackFin and Passion Capital returning. The money pushed Ravelin beyond taxis and food delivery into travel, retail, entertainment and payment providers.
In February 2025, Worldpay agreed to acquire Ravelin. The price was not disclosed, which answers the cost question with an honest blank. The motive was printed in large type. Ravelin brought cloud fraud decisioning and tools for improving authorization; Worldpay brought a network that processed more than 50 billion transactions in 2024. Ravelin later said the deal had completed. In 2025 it reported securing 3.5 billion transactions for 755.2 million shoppers across more than 340 merchants.
This was not a pivot forced by a broken model. It was the distribution plan reaching its logical conclusion. Ravelin had already built multi-year partnerships with Mastercard, Fiserv and Elavon, using their identity data, alerts and merchant channels. Worldpay put the fraud layer beside the payment pipe. Scale, in this case, came wearing an acquirer’s badge.
What a merchant can copy
The copyable part is not Ravelin’s code. Start by measuring false declines beside chargebacks. Feed decisions with the whole customer journey, not merely the card at checkout. Treat links as evidence, not automatic guilt. Keep a few sharp rules for explicit policies and let models handle patterns that mutate. Finally, return outcomes quickly: a chargeback that never reaches the model is a lesson thrown in the bin.
Track fraud loss and acceptance together. A locked shop has a splendid fraud rate and no business.
Shared devices, cards and addresses can reveal coordinated abuse that a single order hides.
Use models for repeatable decisions so analysts can investigate new attacks and policy abuse.
Send disputes, confirmed fraud and recovered accounts back promptly so the system can learn.
There are conditions attached. Custom supervised models need enough representative history and clean labels. A young merchant with sparse orders, delayed chargebacks or inconsistent customer IDs gives the machinery little to learn from. A careless integration can omit precisely the signal that separates a family sharing a tablet from a farm of synthetic accounts. And a company selling offline industrial equipment once a quarter is not Ravelin’s natural habitat. The approach earns its keep where digital volume, repeat behavior and immediate decisions meet.
Ravelin’s founding complaint was that generic fraud software misunderstood a new kind of merchant. Its continuing advantage depends on remembering that lesson. Every merchant has its own normal, and every fraud model is tempted to confuse unfamiliar with criminal. The product’s job is to be suspicious without becoming rude. In ecommerce, that may be a profitable form of good manners.
Keep exploring