The disk tray opened before Roey Eliyahu could do anything about it. He was eleven, chatting online with someone who had sent him a little computer game. The next day came a question: “can I open the disk tray for you?” Then the tray slid out. The game had been a Trojan. Someone else had acquired control of his computer, and had chosen a rather theatrical way to announce it.
There are grander beginnings for a cybersecurity career. This one has the advantage of being easy to understand. A harmless-looking invitation had carried an unexpected privilege. Eliyahu remembered the episode as frightening and fascinating. Years later, the company he co-founded would concern itself with a more complicated version of that same question: what can someone do through a connection that appears perfectly ordinary?
The boy who already had clients
By the time of the disk-tray incident, Eliyahu was already programming. He began at nine in Israel and was doing freelance development at eleven. Making software and discovering its capacity for mischief arrived unusually close together. His early working life offered both the satisfaction of getting a machine to cooperate and a demonstration that cooperation could be obtained under false pretences.
At eighteen he entered an Israeli military cybersecurity unit, later leading development of security systems. He subsequently founded a cybersecurity college and worked on security projects at Cigol Digital Systems. The sequence gave him experience building technology, teaching it and examining what could go wrong with it. By his early twenties, he had become interested in a specific gap: the interfaces through which applications exchange information and carry out instructions.
APIs are rarely the part of an application anyone admires over lunch. They help arrange the ride, fetch the account details, connect one service to another. The convenience on the screen depends on machinery underneath it. Eliyahu saw that this machinery was carrying increasingly sensitive information while much of the security attention remained elsewhere. A useful connection was also an opportunity for an attacker.
A ticket, two meetings, three offers
In his account of the early journey, Eliyahu arrived in Silicon Valley with little money and just two meetings arranged. It is an unpromisingly short calendar for someone crossing an ocean to start a business. He was convinced, however, that he had found a real problem with consequences far beyond one customer. That conviction had to survive the interval before other people shared it.
He also had to decide what sort of company he wanted to build. By his account, three concrete acquisition offers arrived when he was twenty-three. They included the prospect of a well-paid role and money in his pocket. He and his colleagues chose to keep building. The detail matters because the ambition preceded the later valuation: he was already thinking about a substantial independent company while selling remained a plausible alternative.
Looking back, an early refusal can appear wonderfully tidy. At the time it closes one available door without guaranteeing that another will open. Eliyahu's bet was that the problem deserved a company large enough to keep working on it. The practical question was how to turn that conviction into something an enterprise would actually buy.
The useful question came before the pitch
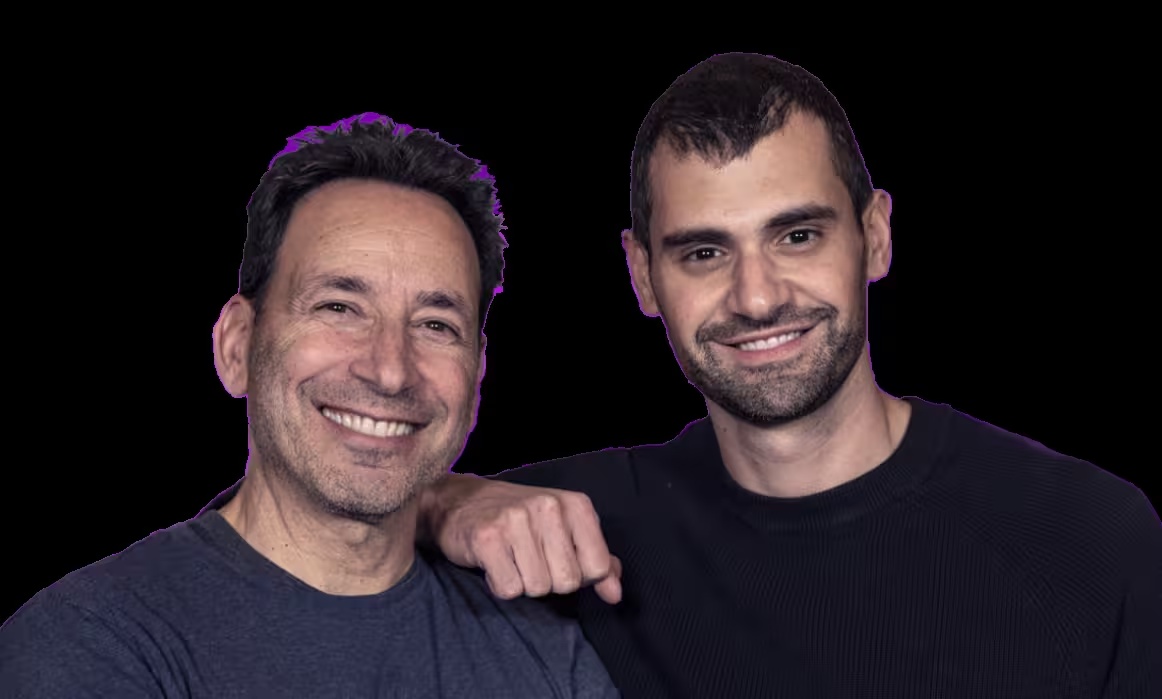
Eliyahu deliberately sought out Michael Nicosia, whose experience included building the sales operation at Adallom. He knew that technical confidence did not supply an education in selling enterprise software. Their partnership put commercial experience alongside his security background. Salt Security was founded in 2016, and Y Combinator lists it in its Winter 2016 batch.
The early customer conversations were less glamorous than the flight. They were also more revealing. Eliyahu asked security leaders, “Is this a problem for you today?” and “How are you solving it now?” Those questions leave room for the inconvenient answer. A founder who has already committed to a diagnosis still needs to discover whether anyone else recognises the symptoms in their own organisation.
The founders' account also puts weight on finding particular people willing to try something new. An impressive company name offers little help if nobody inside it wants to take the risk. An early customer needs both a problem and an appetite for a different solution. The product, meanwhile, has to make adoption manageable. Discovering complicated infrastructure is one task; persuading a busy customer to let you begin is another.
A simplified view of Salt's discovery, posture management and threat protection workflow.
First, give the problem a vocabulary
There was a second difficulty beyond making the technology work. Buyers needed a shared way to describe what they were buying. In his writing about building the API security market, Eliyahu emphasised education: explaining the risk, agreeing on terms and helping organisations judge possible solutions. An unfamiliar category makes every sales conversation carry a small introductory course.
He described work with OWASP on its API Security Top 10 and the investment in Salt Labs, the company's research arm, as part of that effort. Published vulnerabilities could make an abstract warning concrete. A company could see how an interface was abused, then ask whether a similar exposure existed in its own systems. Education became part of the commercial work because understanding the problem was a prerequisite for spending money on it.
The technical argument required a similar change in perspective. A sequence of apparently legitimate requests can reveal more than one request examined alone. Behaviour unfolds over time. Looking for a single conspicuous intrusion can miss an attacker patiently learning how a service works. Eliyahu's argument asked security teams to pay attention to the sequence, including the ordinary-looking steps.
When the numbers caught up
In June 2020, Salt announced a $20 million Series A led by Tenaya Capital. The company then had about thirty employees. By December, Eliyahu had been named to the 2021 Forbes 30 Under 30 list in Enterprise Technology. The recognition put a person's name beside a category that still needed explaining.
February 2022 brought a different scale of endorsement: a $140 million Series D led by CapitalG, Alphabet's independent growth fund, at a $1.4 billion valuation. Existing investors joined the round. Salt reported total funding of $271 million at that point, with $210 million raised during the preceding year. Those are dated financing milestones, useful measures of the backing behind the founders' original wager.
CapitalG partner James Luo explained the investment through the spread of modular software and the security demands it created. Customer feedback, visibility into API inventories and the ability to turn findings into useful action featured in the investment case. The promise had acquired a practical test: could the product help people understand and protect the systems they already operated?
His favourite milestone was a conversation
Asked in 2025 for his favourite company memory, Eliyahu chose a collection of everyday moments with colleagues. Salt had grown to almost two hundred people, he said. What stayed with him were conversations moving between work and personal life. His phrase for them was “the best parts of my day”. For a founder accustomed to explaining an invisible technical problem, this was a pleasantly visible measure of what he had built.
Another early influence helps explain the attraction of making complicated things usable. He remembered the first iPhone's arrival in 2007: intricate technologies assembled into a product people could use without instructions. He also drew a less comfortable lesson from it. Technology keeps being replaced. A successful product has to keep moving as the world around it changes.
“the best parts of my day”
Eliyahu on everyday conversations with colleagues, 2025
There is a basketball game in this argument
Eliyahu is an NBA fan, and his interest extends to the strategy of the game. In a 2023 essay, he used basketball to explain security organisation: players need awareness of one another, someone needs responsibility for coordination, and a team benefits from reviewing what happened on earlier plays. It is a revealing choice of analogy for someone whose work concerns connections.
His point about ownership is particularly practical. APIs can involve product, engineering, networking and security teams. Many people touching the same system does not automatically produce someone responsible for the whole. The captain in his basketball comparison supplies coordination. Watching game film becomes a way to describe learning from published vulnerabilities and other organisations' experience. Even an expensive tool needs a team that knows what it is trying to accomplish.
Now the caller can choose its own next step
By October 2026, Eliyahu was applying his original API argument to AI agents. These systems can choose tools and string actions together, using the same interfaces businesses already depend on. His concern is the resulting chain: which systems an agent reaches, which credentials it carries and whether its next action still belongs within its intended task. Permission granted at the beginning cannot settle every question that arises along the way.
“I still evaluate risk by looking for the chain,” he said that month. In his view, an agent makes this older security problem faster and more concentrated. The interesting weakness may sit between components that each appear reasonable in isolation. The task of protecting an application grows to include the path an autonomous system takes through it.
Salt's October 2026 survey of more than 380 security and technology professionals reported that 49.8% confirmed or suspected an unintended, unexpected or unauthorised agent action in the preceding year. Separately, Salt Labs demonstrated how a malicious email could hijack the Manus agent platform and reach connected accounts. That vulnerability was resolved. The researchers' larger concern was timing: a guardrail detected the attack after code had already executed.
There is an echo of the childhood game here, although the stakes and machinery have changed. An ordinary object carries an instruction. Access turns the instruction into an action. Eliyahu's career has followed that movement from a computer on a desk to the interfaces beneath business software, and now to agents deciding what to do next. The disk tray was an unusually courteous warning. Modern software seldom announces its permissions so clearly.
Keep following the connections
CONVERSATIONS · WRITING · VIDEO