Oege de Moor’s first software customer had a rather particular brief. His father, a professor of Semitic languages, needed to type manuscripts on a computer. The machine could not accommodate the writing he wanted to put into it. Ancient scholarship had encountered a modern inconvenience, and the modern inconvenience was winning.
De Moor wrote him a word processor. It is a small domestic beginning for a career that would involve Oxford, a software company bought by GitHub, and the creation of GitHub Copilot. It also supplies a useful clue. Long before he was selling software to security teams, he was interested in making a computer do something a person actually needed.
Today he is founder and CEO of XBOW, which develops AI systems for offensive security: testing applications by attempting to exploit their weaknesses, with permission. The ambition is to give defenders a way to find problems at the pace software changes. His career has moved from helping people write code to helping them discover what that code might let a stranger do.
The professor who wanted to write programs
De Moor completed his undergraduate studies at Utrecht in 1987 and his Oxford DPhil in 1992. During his Oxford studies he was a Junior Research Fellow at St John’s College; in 1993, Magdalen elected him tutor in computation. Mathematics had caught his attention, and his early research dealt with the foundations of algorithm design.
With Richard Bird, he wrote Algebra of Programming, published in September 1996. The title promises a certain sort of evening. Behind it lies an enduring question: how can mathematical reasoning help people construct programs? His later work would carry that concern out of the textbook and into the untidier rooms where working software lives.
His Oxford research interests ranged across functional programming, program derivation, category theory and predicate transformer semantics. Yet his stated aim was pleasingly practical: better tools and languages for programmers. A mathematical foundation was useful because of what could be built on it. There is a consistency here that the changes in job title can conceal.
Teaching had its own productive consequences. Tutorials sometimes became joint research papers, and some students later joined Semmle. The relationships survived the change from college to company. In 2015, he became an emeritus fellow so that he could concentrate on the business. The professor’s subsequent career would still contain a fair amount of recruiting from the classroom.
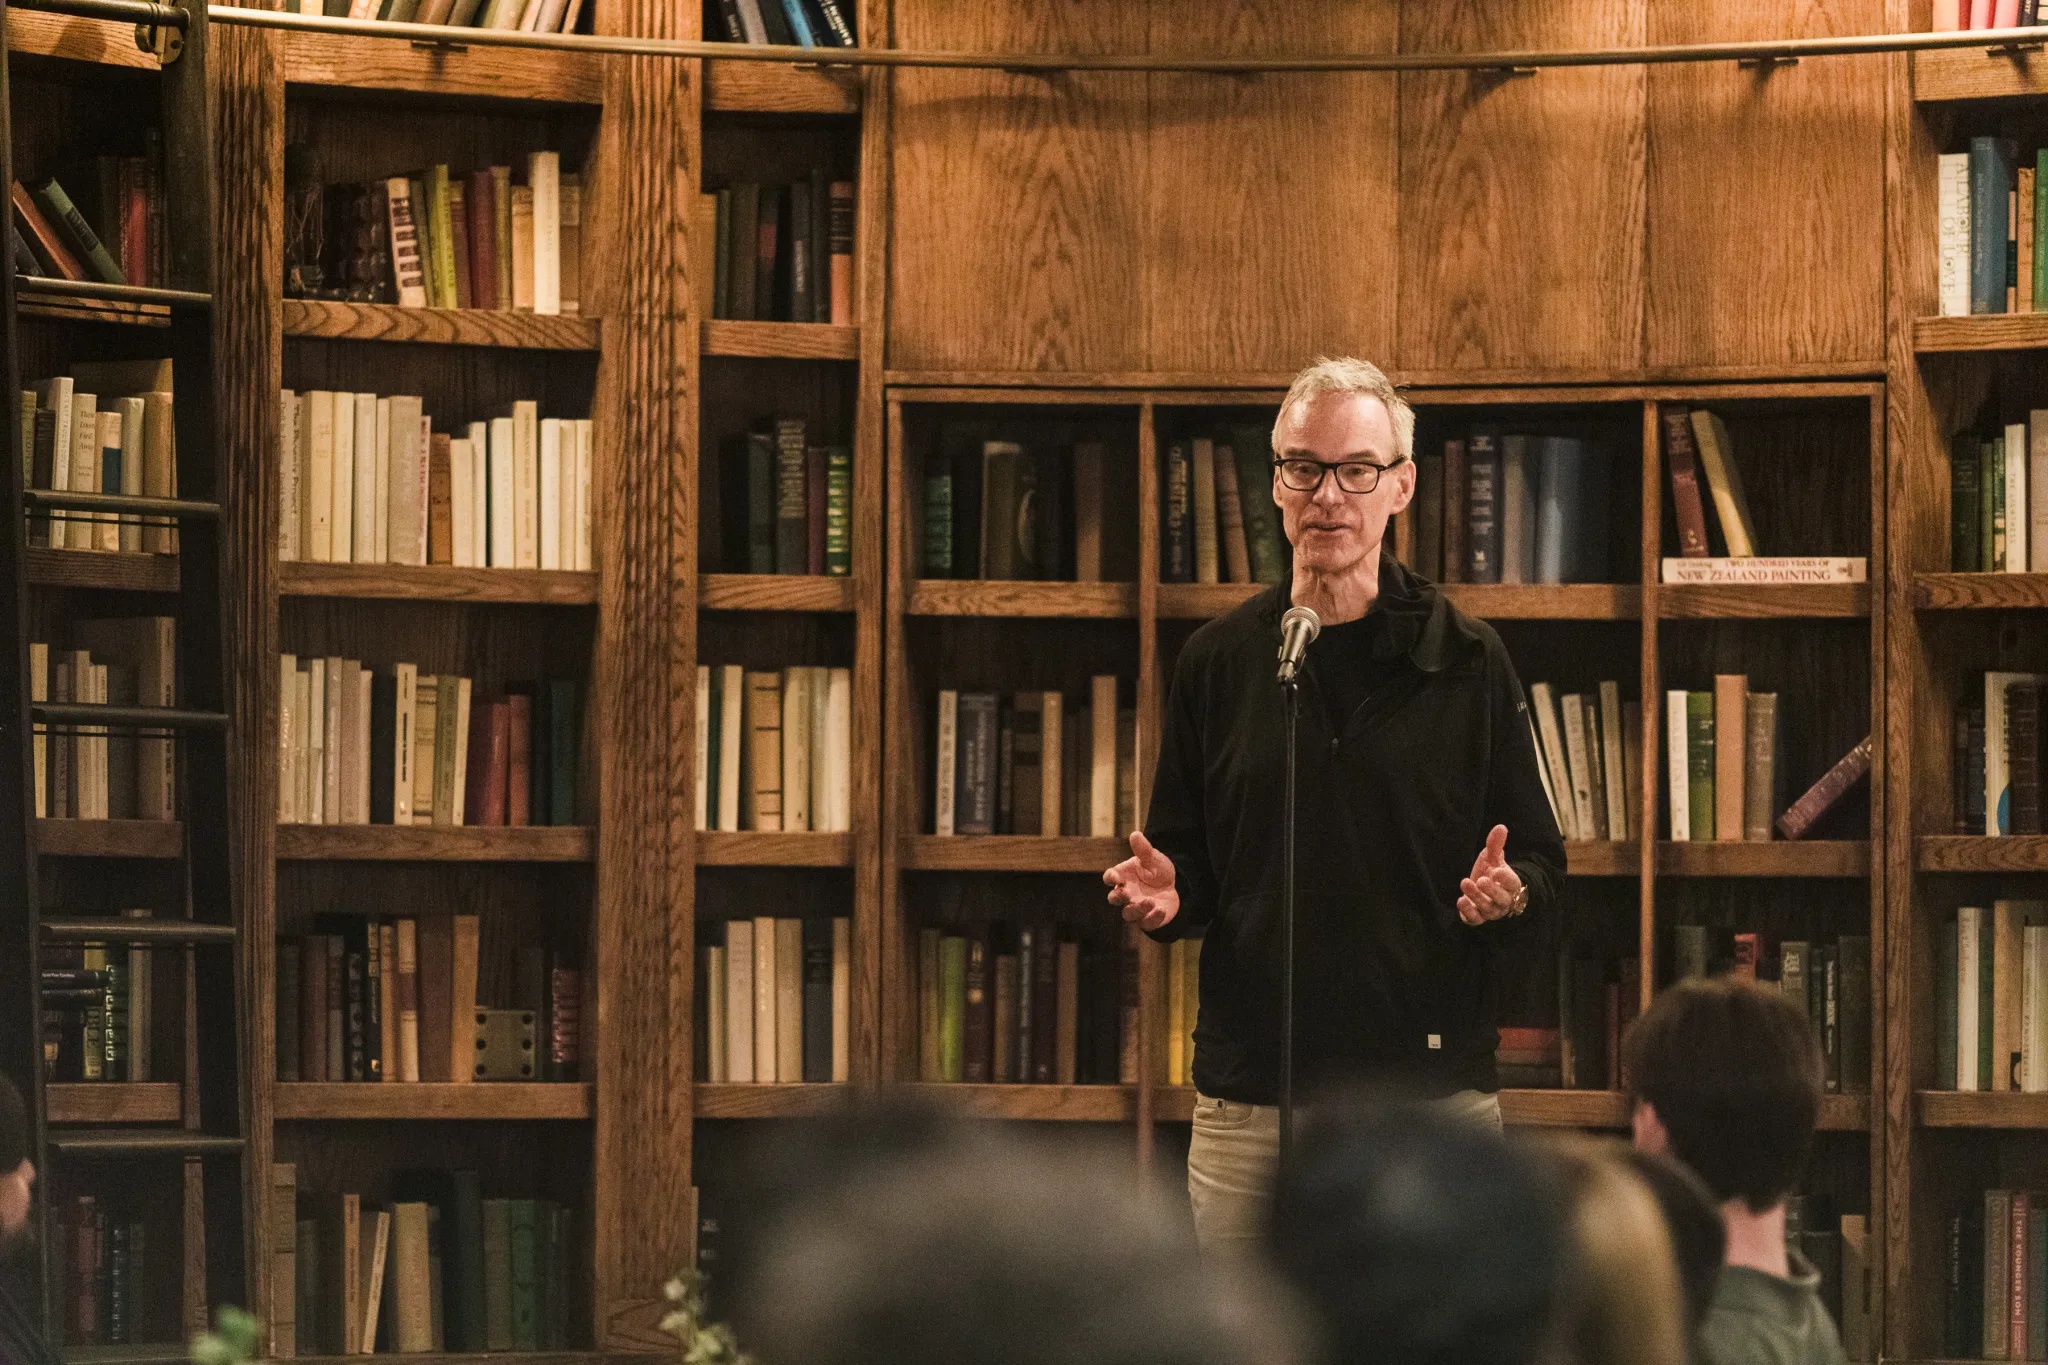
A large codebase, and an impertinent question
A sabbatical at Microsoft supplied the irritation that became Semmle. Working with a complicated codebase, de Moor kept wanting answers about its structure. Finding them took too long. Why should understanding software require so much manual excavation? A database could answer questions about its contents. Perhaps source code could be made to behave similarly.
Semmle began in 2006. The early problem was broad: make unfamiliar code easier to understand. Security became the compelling application. Once a researcher had identified a dangerous pattern, the system could search for other versions of it. One mistake could become a question asked across a much larger body of software.
The underlying idea survives in CodeQL. It builds a database of facts about a program, then lets researchers query those facts for patterns. Data flow and taint analysis help trace how information moves. This matters because a dangerous operation can sit far from the place where untrusted input enters. A text search sees words; a useful analysis has to follow relationships.
The engine took years to work at scale. De Moor has recalled early customer acquisition through cold emails to prospects found on LinkedIn. Theory eventually had to meet an inbox. By September 2019, when GitHub announced its acquisition of Semmle, customers included NASA, Google, Microsoft and Uber. GitHub also reported that the technology had helped identify more than 100 publicly catalogued vulnerabilities in open-source projects.
The acquisition gave the work a different route to developers. GitHub released code scanning into general availability in September 2020, bringing CodeQL into its native workflow. A technique developed to ask questions about code could now sit where people were already reviewing and changing it. Distribution had become part of the engineering problem.
- 01 / SEMMLEAsk the codeQuery a program for patterns.
- 02 / COPILOTHelp write itBring AI into programming.
- 03 / XBOWTest the way inDemonstrate exploitable weaknesses.
The tutor gives the machine an exercise
At GitHub, de Moor led the creation of Copilot. His account of an early experiment has a teacher’s fingerprints: he tried the model on exercises he had used at Oxford. Repeated attempts revealed capabilities that a single answer could obscure. The testing habit was familiar, even if the candidate was unusual.
Copilot put AI assistance alongside the act of programming. For de Moor, it also opened another practical question. At Semmle, finding a potential vulnerability could still leave human researchers with the job of demonstrating an exploit. AI suggested a way to automate more of that work. The next company would grow from the junction of those two experiences.
His argument for the move is straightforward. More people can produce more software with AI assistance, while attackers can use AI too. Security testing must cope with both pressures. For someone who helped make code generation more accessible, the burden of checking the results is an especially close concern. The new work follows the consequences of the old.
A familiar cast, a different assignment
De Moor founded XBOW in January 2024. Nico Waisman, who had worked with him at Semmle and later served as Lyft’s chief information security officer, joined from the outset. Several people from the original Copilot effort came too. The new company assembled around experience in both building AI tools and investigating security failures.
That continuity is part of the story. Albert Ziegler, Andrew Rice and Aqeel Siddiqui appear in the company’s leadership alongside de Moor and Waisman. XBOW’s founding announcement also named Johan Rosenkilde and security researchers Diego Jurado and Joel Noguera. The connections span the mathematical, engineering and adversarial sides of the work. An AI system needs more than a persuasive explanation of why an attack ought to work.
Penetration testing asks what an attacker can actually accomplish against a system. A warning about a possible weakness is useful, but a reproducible demonstration gives engineers something concrete to investigate. XBOW’s product direction is to make that work repeatable and continuous, rather than leave it entirely to occasional assessments booked around people’s availability.
By June 2025, XBOW had reached the top of HackerOne’s global leaderboard. The ranking was a public milestone for its bug-bounty work. It should also be read with the relevant distinction intact: in its account of more than 1,060 reported vulnerabilities, XBOW said discovery and exploitation were automated, while humans reviewed submissions for compliance. The review remained part of the process.
The company grows into its argument
In March 2026, XBOW announced a $120 million Series C led by DFJ Growth and Northzone, at a valuation above $1 billion. Two months later, it added $35 million from strategic investors including NVentures, Samsung Ventures, Accenture Ventures and SentinelOne S Ventures. A company valuation is a price attached to an investment; the practical question remains what the software can do.
The May announcement gave some indication of the business taking shape: more than 100 customers worldwide and more than 250 employees. Samsung’s role included distribution in South Korea. The challenge was extending beyond an impressive demonstration to selling, deploying and supporting security testing across organizations with different systems and requirements.
By September, XBOW was introducing Autonomous Exposure Management, intended to test an enterprise’s external application estate rather than one application at a time. Its description begins from an attacker’s outside perspective, without source code or credentials. Customers approve the target list before testing. The product reflects de Moor’s continuing interest in widening the amount of useful work a tool can perform.
October brought data residency options for Australia, Canada and Japan. That is a quieter announcement than an exploit or a financing round, but a revealing one. An enterprise can admire a security product and still have requirements about where assessment records are stored. Eventually, even an autonomous hacker has to satisfy the procurement department.
Six days, after the groundwork
At an all-hands gathering in Malta at the beginning of 2026, de Moor challenged the team to build a full-chain Chrome exploit by August’s Black Hat conference. The assignment pushed beyond web applications toward native software. In October, XBOW announced that the work had earned a $250,000 bounty from Google, and said the bugs had been fixed.
The six-day construction of the awarded chain followed earlier research and an initial chain containing a bug Google already knew about. Researchers had prepared interchangeable components, which helped them replace the disqualified route. AI searched code and developed candidate exploits; people chose strategy, checked work and redirected the effort. The result belonged to that combination.
It is a fitting place to find de Moor now. The professor who studied how programs could be reasoned about is asking what happens when machines help test the boundaries of software in practice. His wager depends on defenders using the same falling cost of discovery that attackers can exploit. The objective is useful evidence, obtained soon enough to act.
There is still room for a song
De Moor is based in Sliema, Malta. Away from the security argument, his public enthusiasm for AI includes Suno, the music-generation service, and Harmonic’s work on mathematical reasoning. In one interview, he said he had used Suno to send his wife a song about sitting on their balcony. The application was modest, personal and rather charming.
He has also spoken warmly about personalized tutoring. It connects the Oxford years to his interest in what AI might make more widely available. The appeal is recognizable: give more people access to a kind of help that would otherwise be scarce. That idea can take the form of a tutorial, a programming assistant or a security test.
His old Oxford research page contains an economical description of the impulse: “I like applying theory, especially when it is driven by good applications.” Decades of companies and products fit inside that sentence. The applications have grown more complicated. The pleasure of making something useful remains easy to recognize.
“I like applying theory, especially when it is driven by good applications.”
Oege de Moor · Oxford research profile
Keep following the questions
Read XBOW and de Moor’s account of the Chrome research. Watch the XBOW Founder Spotlight interview or listen to his Training Data conversation.
Find him on LinkedIn, X and GitHub. Visit his Magdalen profile and the Algebra of Programming page.