The most dangerous spreadsheet in a company is rarely the one with bad arithmetic. It is the one everyone quietly treats as the truth. A vendor list lives in one tab. Security controls live in another. Audit evidence arrives by email. A policy owner leaves, a deadline slips, and the board still gets a reassuring red-yellow-green chart. This was the habitat in which LogicGate was born.
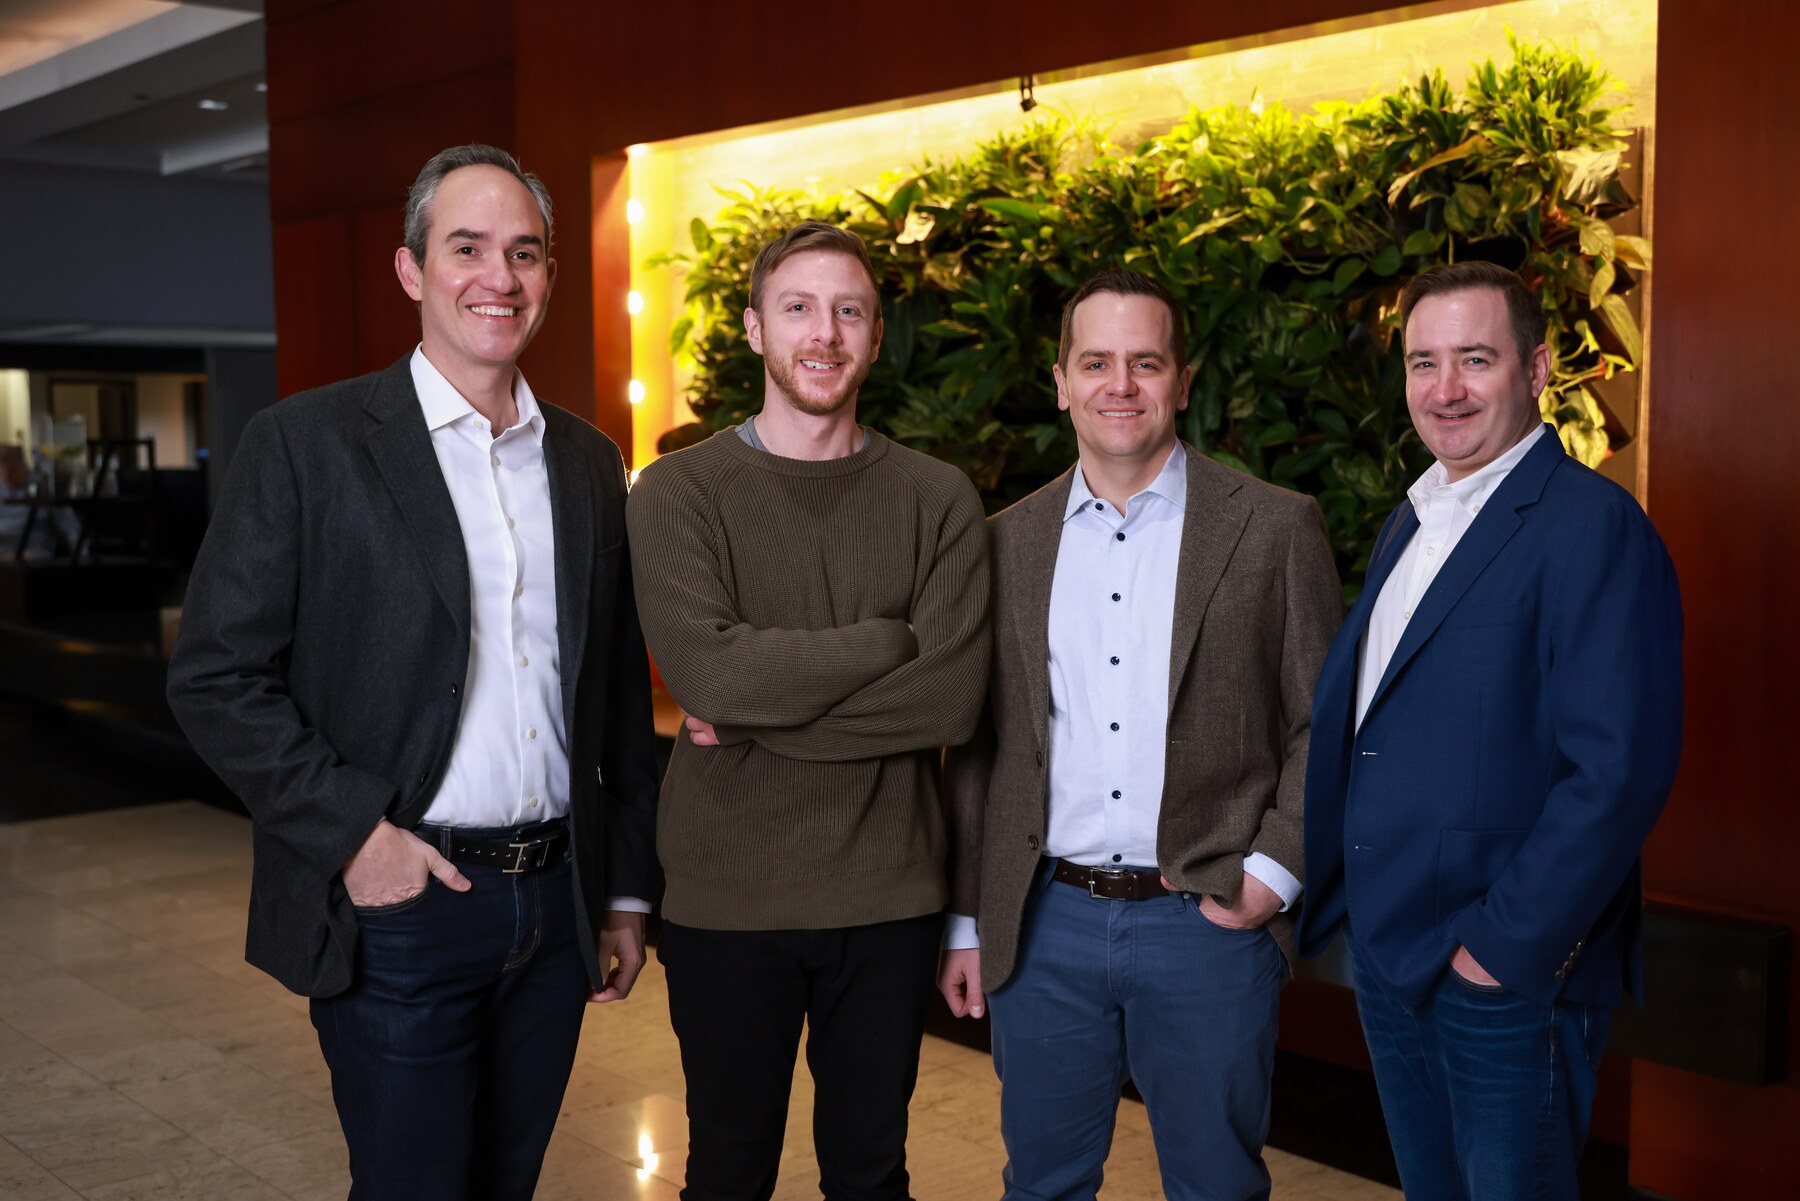
Before they were software founders, Matt Kunkel, Jon Siegler, and Dan Campbell were governance, risk, and compliance consultants. Their clients had bought point solutions, but the real work still required Excel, developer customization, and what the founders later called “duct tape and bubble gum.” The failure came first: off-the-shelf tools could record a prescribed process, yet struggled when the business changed the process.
The trio started LogicGate in Chicago in 2015 around a deceptively plain idea. Let risk teams shape software around their work without opening a development ticket every time a regulation, vendor, control, or approval path changed. The company’s current product, Risk Cloud, turns that idea into a no-code SaaS platform for governance, risk, compliance, cyber, audit, privacy, resilience, and, lately, AI governance.
What it actually sells
Risk Cloud is not one checklist in a blue suit. It is a platform with more than 40 purpose-built applications. A customer can begin with third-party risk, for example: collect a vendor request, route it by criticality, send the right questionnaire, pull in an outside cyber rating, create findings, assign remediation, and report the remaining exposure. The same underlying records can connect to controls, policies, assets, incidents, regulations, and enterprise risks.
That relationship model matters. Traditional registers treat a risk as a row. LogicGate uses graph-database technology so a team can see the web around it - the affected asset, the failed control, the vendor involved, the policy obligation, and the business owner. Dashboards and reports then draw from one connected repository instead of a monthly reconciliation ritual.
The product thesis / one risk, many consequences
A graph is useful when one change should ripple visibly. It is less useful when the underlying records are stale, duplicated, or owned by nobody.
The menu spans policy management, enterprise and operational risk, cyber risk, third-party risk, controls compliance, regulatory compliance, internal audit, data privacy, operational resilience, ESG, and AI governance. Customers can take a preconfigured application or have LogicGate’s in-house practitioners tailor one. Integrations connect tools such as Jira, ServiceNow, AWS, OpenAI, Black Kite, and SecurityScorecard. An API supports custom plumbing.
Who buys the map
The buyer is usually not a lone compliance manager chasing a first SOC 2 badge. LogicGate is built for teams whose risk domains have begun to collide: cybersecurity needs vendor context; procurement needs faster assessments; audit needs evidence; legal needs policy attestations; executives need financial impact. Public stories feature organizations including Equiniti, Intradiem, Team Select Home Care, and Hyatt. Regulated industries - finance, healthcare, insurance, energy, pharmaceuticals, and large technology businesses - are the natural terrain.
The commercial model is enterprise SaaS, sold by quote. LogicGate does not publish a tidy per-seat price, and that is itself useful buyer intelligence. The bill can involve selected applications, builder or power-user access, particular AI capabilities, integrations, implementation, and support. Some solution packages include unlimited ordinary users, which helps when evidence and approvals must reach far beyond the risk team. But anyone asking “what does it cost?” needs a scoped proposal, not a blog estimate.
The service layer is part of the product, not an apology for it. LogicGate uses its own GRC practitioners for implementations and trains customer “power users” to keep adapting the system. Consulting and delivery partners including Crowe, PwC, Protiviti, and Optiv extend that reach. Technology partners fill gaps the platform should not pretend to solve alone: Black Kite and SecurityScorecard contribute outside intelligence about vendor security, while tools such as Jira and ServiceNow carry work into the systems employees already use.
Inside the company, six published values begin with “Own It” and end with “Do the Right Thing.” The list also asks employees to embrace curiosity, act as one team, raise the bar, and empower customers. Those phrases could decorate any office kitchen. Here they at least rhyme with the product architecture: let people closest to a process change it, then make the consequences visible to everyone else. LogicGate’s culture report also describes employee resource groups and formal inclusion work. The harder cultural proof is whether a company selling accountability practices it during its own leadership handoff.
“The value drive is to have a centralized data repository that can meet all of the different challenges.”Matt Kunkel, co-founder and executive chairman
LogicGate sits between two market poles. Archer, MetricStream, ServiceNow IRM, Diligent, IBM OpenPages, Riskonnect, and Workiva offer broad enterprise suites. Vanta, Drata, Hyperproof, and Sprinto often begin with faster compliance evidence automation. LogicGate’s wedge is enterprise breadth without surrendering every configuration change to specialists. That makes it attractive to a growing company that expects its risk program to mutate.
The AI arrives wearing a visitor badge
In 2020, after months of customer conversations during the first stretch of the pandemic, LogicGate renamed its suite Risk Cloud and sharpened its pitch from managing compliance to treating risk as strategic information. The 2026 shift is larger. Spark AI can summarize records, spot linkages, produce reporting insights, and test evidence. Seven early-access Workflow Agents arrived across third-party risk, enterprise risk, business continuity, and AI governance.
The examples are concrete enough to examine. One customer with four people managing more than 2,200 vendors estimated that third-party agents could save at least 2,000 hours a year. Another, facing a backlog of more than 100 AI use cases, projected a 75 percent reduction in assessment time. These are customer projections reported by LogicGate, not independent time studies, but they illuminate the target: repetitive intake, routing, first-pass assessment, and documentation.
Config Newton goes one layer deeper. LogicGate calls it an agentic GRC engineer. It can draft a blueprint, build applications through APIs, generate documentation, and refine workflows from natural-language prompts. The company’s implementation teams use it now; direct customer availability is planned for 2027. Crucially, a human must approve the blueprint before a build and review the result afterward. In a market fond of autonomous-everything confetti, that checkpoint is not a footnote. It is the product promise.
The catch: flexibility is not strategy
No-code can remove a developer bottleneck. It cannot decide who owns a risk, settle a broken taxonomy, persuade a business unit to submit evidence, or make an executive care. A flexible platform can even accelerate disorder by allowing every team to recreate its favorite spreadsheet in a new place. LogicGate works best when the buyer has a named process owner, a shared vocabulary, data worth connecting, and the willingness to govern its own configurations.
Conditions that fit
- Several risk domains need shared records.
- Workflows change with rules and growth.
- A team can own taxonomy and design.
- Executives want quantified impact.
Conditions that fight it
- The goal is only a quick certification.
- Source data is unreliable or orphaned.
- No one owns cross-team adoption.
- An existing platform already runs the work.
It may also be more platform than a small security team needs. A startup collecting evidence for one framework can favor a lighter compliance tool. A company standardized deeply on ServiceNow may prefer to keep risk inside that operating system. A mature multinational may choose the heavier content libraries and specialized depth of an older suite. The right comparison is not a feature bingo card. It is the operating model the buyer can sustain.
What to copy before buying anything
LogicGate’s most portable lesson predates Risk Cloud. Its founders spent years inside the ugly work, noticed where purchased tools forced customers into unofficial workarounds, and productized the recurring pattern. A risk leader can borrow that method without signing a contract; a founder can borrow it without knowing what GRC stands for.
Find the stubborn spreadsheet.Look for the file that survives every transformation project. It exposes the gap between the official process and the real one.
Map relationships before screens.Define how risks, owners, controls, evidence, vendors, and outcomes connect. A nicer form will not repair a broken model.
Automate the repeatable middle.Use rules or agents for intake, routing, reminders, first-pass review, and documentation. Keep appetite, exceptions, and accountability with people.
Measure hours and exposure.Count cycle time, backlog, avoided rework, and risk reduction. “Better visibility” is too polite to win the next budget.
The company has had money to pursue the thesis. LogicGate raised $1.9 million in seed capital, $7.5 million in a 2018 Series A, $24.75 million in a 2019 Series B package, and a $113 million Series C led by PSG in 2021. It has since earned analyst recognition across GRC and third-party risk, won a 2025 ISACA award for AI governance, and appeared on the Inc. 5000 six years running. In July 2026, Diego Panama became CEO while Kunkel moved to executive chairman.
That transition leaves LogicGate with a crisp test. It already proved that configurable workflows can liberate risk teams from some spreadsheets and developer queues. Now it must prove that agents trained on a decade of implementation experience can reduce the next bottleneck without creating a more consequential one. The reader should copy the restraint: automate what can be audited, preserve the judgment that cannot, and never confuse a connected map with the territory.