A database is copied for a test. The test ends. The database remains. In the cloud, this is an ordinary sequence of events, which is precisely why it deserves attention. The original records may be carefully guarded; their offspring may have wandered into a different account, acquired different permissions, or lost their owner. Laminar built its business around that small administrative embarrassment: companies could possess sensitive information without knowing where they possessed it.
- Find sensitive data, including the copies nobody catalogued.
- Rank exposure by what the data contains and who can reach it.
- Now part of Rubrik, connect data posture with recovery.
That problem has a name, shadow data, though the name makes it sound more theatrical than it usually is. An abandoned backup is enough. So is a useful dataset moved somewhere unsuitable. Laminar’s proposition was that security should follow the contents as those contents move, rather than depend on yesterday’s list of approved storage locations.
01 / Two friends, one blind spot
Amit Shaked and Oran Avraham founded Laminar in 2020. Their launch announcement dates their friendship to fourteen. Both later served in Israel’s Unit 8200; Shaked worked at Magic Leap, Avraham at Medigate. Avraham also led a team that won four of six Google Capture the Flag competitions. Their expertise covered both attacking systems and understanding how businesses use them.
The origin was less glamorous than the credentials. In a 2023 interview, Shaked described conversations with CISOs who lacked visibility into cloud data. He also named the early practical obstacle: persuading talented people to join uncertain product development and fundraising during the pandemic. The company needed people willing to build before it had much certainty to offer them.
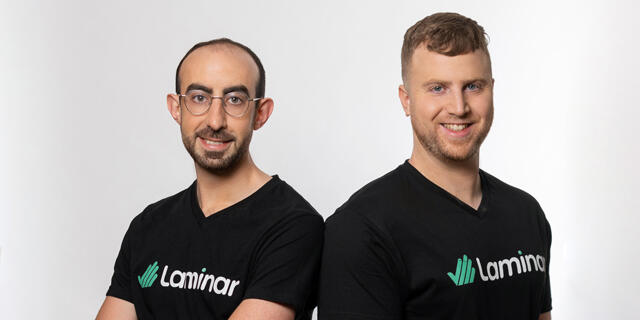
There was something appropriately domestic about their working environment. The Tel Aviv office design used quiet rooms organized around teams. A reception sofa could split into three pieces for gatherings. Even the furniture acknowledged that things would move around. The important question was whether anyone could still account for them afterward.
02 / Look inside the bucket
Consider two publicly accessible storage buckets. One holds brochures. The other holds customer information. Infrastructure checks can identify the public setting; knowing the contents changes the urgency. In research published by Laminar, personally identifiable information appeared in 21% of the public-facing buckets examined. That finding describes the studied buckets, not all cloud storage. Its lesson is simple: exposure becomes meaningful when you know what is exposed.
contained personally
identifiable information
Laminar connected through cloud APIs and used agentless, asynchronous scanning. Its stated architecture kept source data within the customer’s environment. By July 2023, its supported landscape included AWS, Azure, Google Cloud, Snowflake, BigQuery, and SharePoint Online. This was software for security, privacy, and governance teams overseeing enterprise data spread across multiple services.
Its five-function platform followed a useful sequence. Data landscape intelligence assembled the inventory. Posture management assessed policy violations and ranked risk. Access governance examined human and machine permissions. Detection and response watched for suspicious activity. Privacy and compliance connected those findings to obligations and reporting. A discovery became more useful when it came with access context and a practical next step.
- 01DiscoverWhere is it?
- 02ClassifyWhat is inside?
- 03PrioritizeWho can reach it?
- 04RemediateWho fixes it?
03 / Seven petabytes of missing context
Financial services makes the appeal easy to understand. Customer records matter, permissions multiply, and cloud estates are difficult to inspect by hand. Pagaya publicly endorsed Laminar in 2022. Rubrik later published an anonymous global fintech case reporting seven petabytes discovered, classified, and secured, alongside 90% more data visibility. These are vendor-reported results for one customer, rather than a forecast for the next buyer.
The commercial model fits that audience: enterprise software purchased through licensing and sales conversations. Evaluation should include deployment scope, cloud scanning costs, and the work of correcting findings. A license buys capabilities; the organization still has to decide who owns a sensitive dataset and whether its access is justified.
Laminar occupied the data security posture management market, alongside alternatives such as Cyera and BigID. Agentless discovery alone is no longer a distinctive claim. Rubrik’s more concrete proposition is the combination of data posture and recovery. Infrastructure posture tools remain useful too: configuration and contents answer related questions, and a buyer needs both answers.
04 / A buyer with the other half of the problem
Laminar had raised $67 million by June 2022: $5 million in seed capital, a $32 million Series A, and a $30 million extension. In July 2023, Shaked was still describing ambitions for an independent company. On August 8, Rubrik announced its acquisition agreement. The explanation offered publicly was complementary capabilities: Laminar supplied cloud visibility and control; Rubrik brought a broader recovery business.
“We have found synergy with Rubrik”Amit Shaked, acquisition announcement, August 2023
Rubrik’s later filing puts acquisition-date purchase consideration at $104.9 million, including $90.8 million in cash and the rest in stock. It separately identifies a $23.8 million service-based holdback excluded from that cash amount. Purchase accounting and employee-related payments deserve separate treatment. The acquisition also gave Rubrik a team around which to establish an Israeli research and development center.
05 / The lesson travels with the data
The useful part of Laminar’s approach is copyable. Start with one supported environment. Find an unknown sensitive asset, check the classification, identify its readers, assign an owner, and follow a correction through to verification. Rubrik’s policy documentation distinguishes misplaced, overexposed, obsolete, and misconfigured data. That vocabulary gives teams specific problems to solve instead of a general instruction to become more secure.
This work depends on coverage, permissions, accurate classification, and people who act on findings. A system cannot assess a store it does not see; an alert cannot negotiate ownership. Buyers should also examine scan overhead and activity visibility. Continuous discovery needs a working process around it, and posture management belongs alongside incident response and recovery planning.
By July 2025, Rubrik was applying the same concerns to Microsoft 365 and Copilot, with classification, labeling, and access controls aimed at oversharing. AI gives misplaced information another route to travel. Laminar’s original question therefore remains wonderfully plain: before letting your data do something useful, do you know where it is, what it contains, and who can get to it?
Follow the data
Explore the product, the company, and the conversations behind it.