An employee leaves. Their laptop goes back. Their calendar stops filling up. Somewhere, an application may still remember them as a person entitled to enter. That little mismatch between an organization’s intentions and its software is the territory Simeio occupies. Identity security sounds like a matter of checking credentials. The more revealing question comes afterward: what should this person be allowed to do, and who makes sure the answer changes?
- Simeio designs, connects and runs enterprise identity systems.
- Its orchestration platform coordinates tools across vendors.
- The buyer is an organization with complex access needs and an ongoing operations problem.
The trouble between the tools
A company can have a product for signing in, another for reviewing permissions, and another for protecting administrator accounts. Each solves a legitimate problem. Together, they create a second problem: somebody must connect them. A promotion, a departure or a newly acquired business has to become the right change in every relevant system. Otherwise, the organization is left translating policy into tickets.
Simeio sells that connective work. Its services cover assessment, implementation, migration and ongoing management. The technical vocabulary includes identity governance and administration, access management, privileged access management and customer identity. In everyday terms: decide who gets access, help them authenticate, constrain powerful accounts, and keep customer logins usable. Enterprises and government organizations are its audience. Financial services, healthcare, retail and transportation all appear in its customer material.
Its own software, Identity Orchestrator, supplies a shared operating layer. An application inventory brings scattered systems into view. Integrations connect identity products. Onboarding workflows, control monitoring and an evidence repository organize work that might otherwise happen separately. This is the interesting market position: Simeio can implement products from companies such as SailPoint, Saviynt, Ping, Okta and CyberArk while adding coordination around them. The software vendor and the operator can be different businesses.
A bank buys continuity
Consider an unnamed financial-services client in Simeio’s case studies. Its provisioning was fragmented, access reviews were burdensome, and manual workflows were filling support queues. A former chief information security officer recommended Simeio after working with it previously. The engagement continued beyond that sponsor’s departure. A team of more than 20 specialists worked under a multi-year managed-services agreement.
The work included moving governance from Oracle Identity Manager to Saviynt, improving privileged-access integrations, and building a separation-of-duties policy engine. Simeio reports $2 million in annual savings associated with those policies and more than a 50% reduction in privileged-access licensing costs. These are vendor-reported results for one anonymous client. They illustrate the kinds of costs the work can address; a buyer still needs a scoped proposal to judge its own economics.
There is a useful clue in the sequence. The initial failure was operational: permissions, reviews and support were becoming difficult to manage. The response combined replacement, integration and continuing labor. The commercial model follows that shape, with project work alongside ongoing service contracts. For buyers comparing bids, implementation fees belong beside software licenses, internal staffing, support and the cost of maintaining integrations.
A sensible procurement conversation would separate three questions. What will the team install? What will it operate? What result will the contract measure? A cheaper rollout can become an expensive dependency if nobody owns changes afterward. Equally, a broad managed service can be unnecessary if an internal team already handles the work well. The comparison should follow the actual workload, including the awkward applications that resist standard connectors.
The people behind the permissions
Simeio’s roots precede today’s enthusiasm for AI agents. ZMC dates its founding to 2007. Founder Hemen Vimadalal had previously worked on identity company Vaau. Private equity firm Welsh, Carson, Anderson & Stowe invested in 2015; ZMC acquired Simeio from WCAS in 2020. In 2023, Simeio bought PathMaker Group, adding consulting and SailPoint implementation expertise. These transactions accumulated both capital and people who knew how enterprise identity systems behaved.
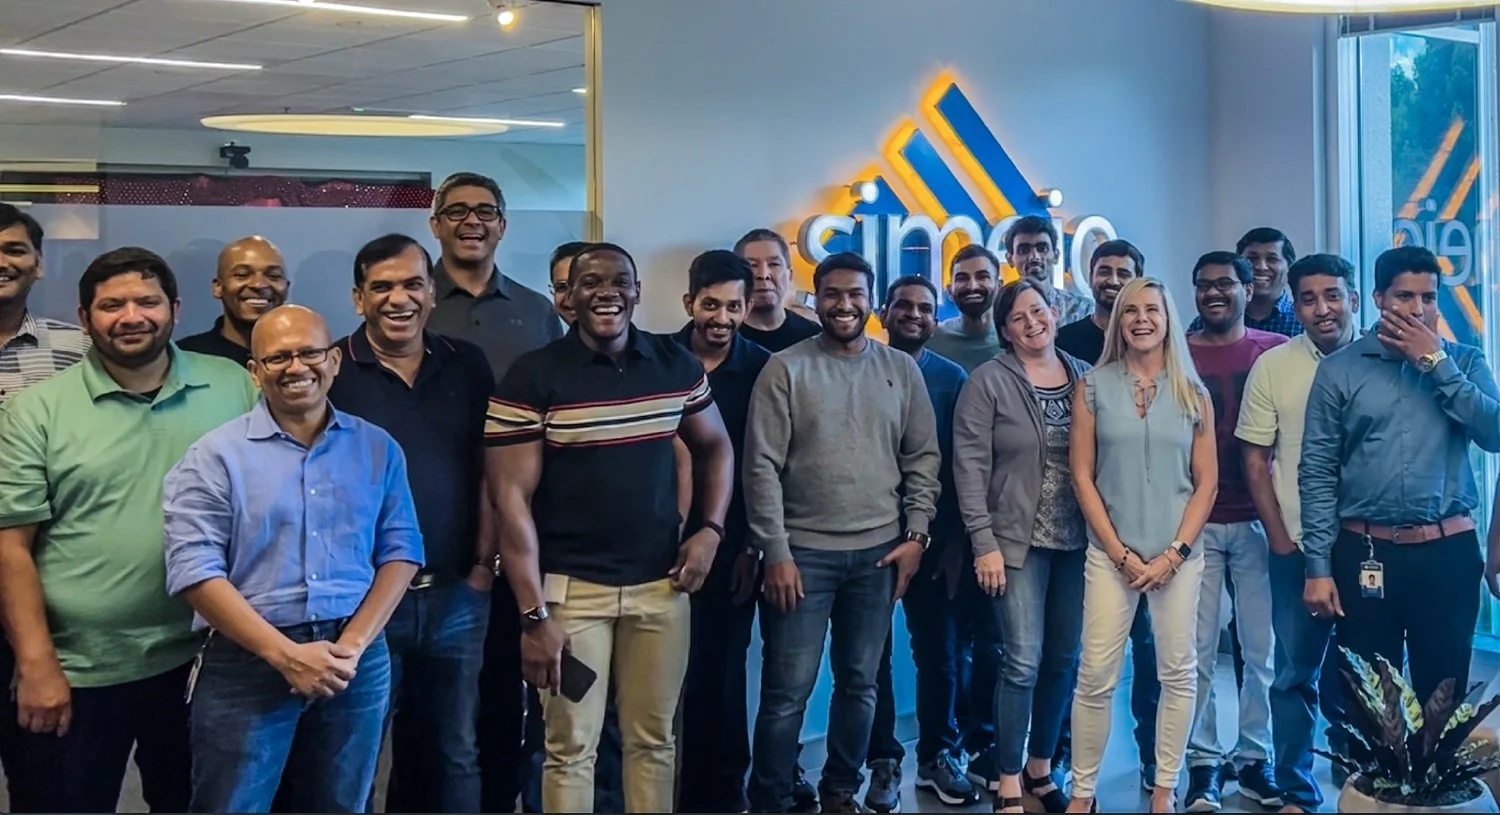
People also became a stated point of correction. In April 2026, CEO Nick Rowe described client demands for more continuing value. Simeio responded with dedicated resources, identity specialists throughout engagements and contracts linked to business outcomes. Rowe reported Net Promoter Scores of 25 in 2023, 39 in 2024 and 51 in 2025. The progression is company-reported; it suggests a useful question for any services buyer: what, precisely, changes when the customer is unhappy?
Who owns the result after the launch meeting?
The daily work can be surprisingly ordinary. One healthcare case describes a round-the-clock helpdesk supporting 150,000 employees and 25,000 healthcare professionals. Careers material emphasizes learning and development. A workplace survey profile updated in September 2023 reported that 72% of employees considered Simeio a great place to work. Service quality depends on keeping expertise available, including when the ticket is thoroughly unglamorous.
The new colleague has no payroll record
Customer identity adds another scale. A transportation engagement covered more than 80 million accounts. Its password-based framework needed stronger protection. Simeio used PingOne DaVinci and PingOne MFA to introduce risk-based authentication steps across websites and mobile applications. The practical aim was to strengthen sensitive interactions without making every journey through the service unnecessarily awkward.
Now the population also includes software. In August 2026, Simeio announced a partnership with Clutch to address machine identities, service accounts, secrets and AI agents. That same month, it announced Saviynt’s first Certified PAM Delivery Partner designation, a program requiring demonstrated customer implementation. Both developments extend its existing specialty: turning identity technology into controls an organization can actually operate.
That expansion makes ownership more interesting. An employee has a manager and a departure date. A service account may persist because an application needs it to function. For a prospective buyer, the useful demonstration would show how such an account is discovered, assigned an owner, reviewed and disabled safely. A dashboard matters only if someone can take the next action. The same operational test applies whether the identity belongs to a contractor or a piece of software.
Start with one application
The lesson readers can copy is modest. Inventory an application. Name its owner. Record who should enter, how access is approved, how it is reviewed, and how it ends. Then test the whole sequence. Our assessment: Simeio’s model makes most sense when that exercise exposes repeated coordination problems across many systems. A small business with straightforward access needs may find an internally managed platform sufficient. Outsourcing also requires clear authority, reliable application information and agreed outcomes. Someone must still decide what access is appropriate.