A password has a peculiar talent for surviving its purpose. The deployment finishes. The engineer moves teams. The experimental service disappears. Somewhere, a credential remains perfectly willing to let someone in. In automated infrastructure, the question is less whether anyone remembers that password than whether the system still accepts it.
Defakto Security has built its business around changing that arrangement. Software should establish what it is, receive permission for a particular task, and lose that permission when it is no longer needed. The company calls this non-human identity and access management. The plainer description: give machines identities that do not require a permanent password tucked into a drawer.
- The job: authenticate services, pipelines, workloads, and AI agents with short-lived identities.
- The mechanism: verify runtime context, issue identity, apply policy, and record access.
- The business: enterprise subscription software built around open identity standards.
- The test: can your team retire a credential without making the application harder to run?
The password that keeps its job
Consider a familiar engineering arrangement: a build pipeline needs access to a cloud service, so someone supplies an API key. Possession of the key becomes the admission ticket. The key can be copied, passed through an environment variable, or left in a configuration file. Its relationship with the original task grows increasingly distant.
This is an illustrative workflow, rather than a reported Defakto customer incident. It explains the company’s target neatly. A secrets manager can improve storage and rotation. But the application still depends on a credential that must reach it somehow. Defakto wants to reduce the occasions on which that enduring credential has to exist at all.
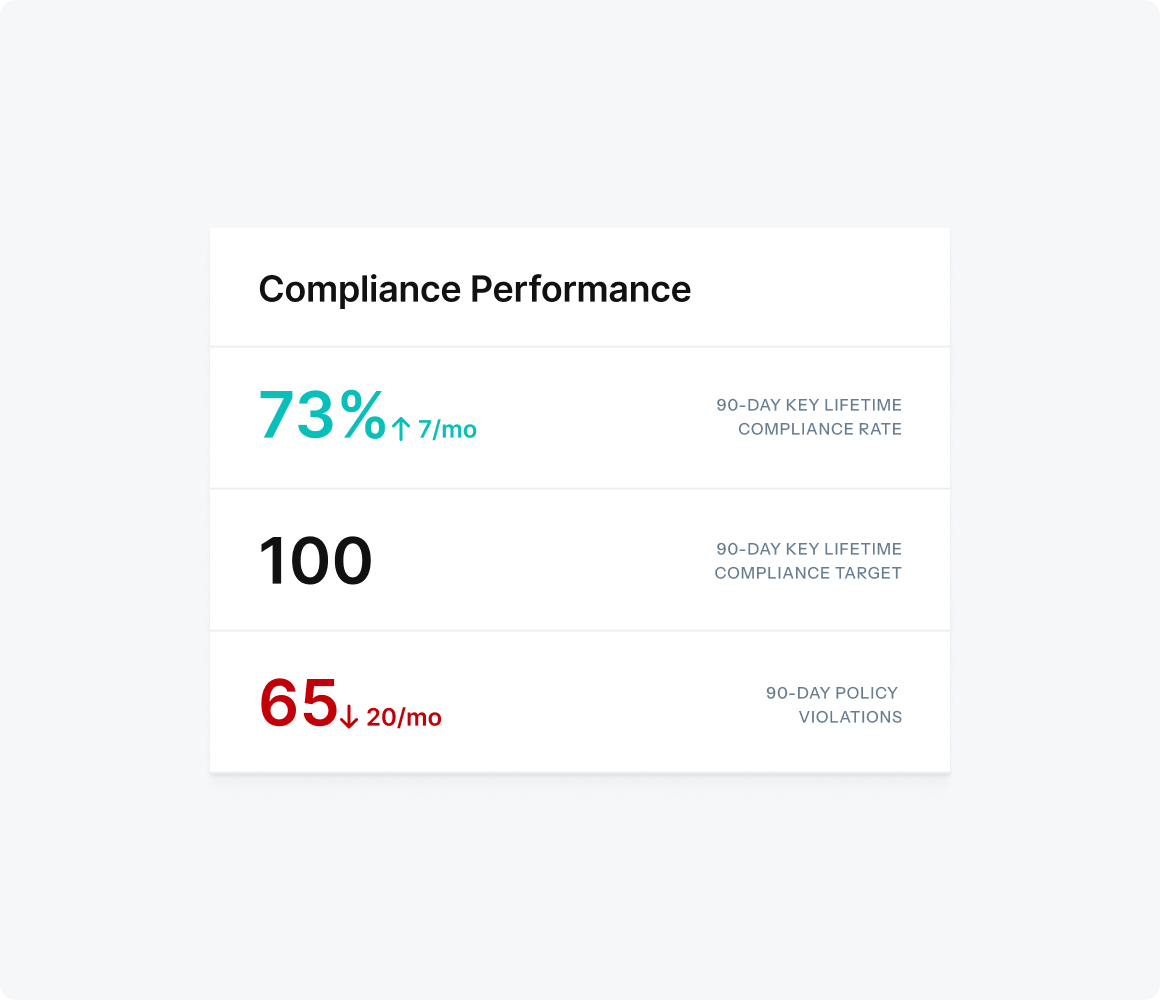
Its approach starts with runtime verification. A workload proves its identity through evidence about its environment; the platform then supplies a short-lived cryptographic credential. The receiving system can verify that identity and apply an access policy. The business benefit is a smaller inventory of permanent permissions and less credential housekeeping. The engineering benefit is fewer passwords travelling through the delivery process like unattended luggage.
A good standard meets a difficult deployment
The origin is an adoption problem. Defakto’s account of its founding points to Eli Nesterov’s experience managing identity at ByteDance’s infrastructure scale. Open-source approaches offered the desired security model, but implementing them required substantial work. Danny Oliveri saw an opportunity to turn that technical foundation into something enterprises could buy and deploy.
The distinction matters. An open standard describes how systems can cooperate. A usable product must also handle installation, configuration, operations, and the people who will receive a call when cooperation stops. Defakto’s wager is that companies want workload identity without assembling the entire operating machinery themselves.
The foundation is SPIFFE, an open framework for software identity, with SPIRE providing an open-source implementation. These standards support verifiable identities across different hosting environments. Defakto packages its own enterprise offering around that broader ecosystem. The customer is buying implementation and management, rather than ownership of the idea that software should have an identity.
Five verbs, one identity problem
The product names are refreshingly short. Ledger discovers identities and supports ownership and governance. Mint issues identities. Ship applies the approach to builds and deployments. Trim addresses excessive access. Mind extends it to AI agents and language-model workloads. A shared Console brings the administrative view together.
The sequence is useful because issuance alone cannot answer every security question. Before granting access, someone needs to know which workload exists, who owns it, and what it should be allowed to do. Afterwards, someone needs a record of the action. A beautifully signed identity attached to a wildly permissive policy remains an expensive way of saying yes.
- 01Verify contextEstablish the workload’s origin
- 02Evaluate policyCheck what it may request
- 03Issue identitySupply a short-lived credential
- 04Authenticate & logAllow access with attribution
The target users are security teams, platform engineers, and identity administrators. Their concerns overlap without being identical: security wants smaller exposure, engineering wants deployments to keep moving, and IAM wants ownership and reviewable permissions. Defakto reports production use at Global 2000 organizations. Its website also presents anonymous testimonials from retail and technology companies and a Fortune 100 security leader.
The rival is also your own engineering team
Defakto sits where workload identity, secrets management, and enterprise access governance meet. Its pitch is broader than scanning for exposed keys: it proposes replacing the underlying authentication pattern. For an enterprise spanning clouds and private infrastructure, a consistent identity model may be more attractive than several unrelated credential systems.
That distinction does not make the company alone in the field. Aembit also markets workload IAM and secretless access. Teams can operate open-source SPIRE themselves, use native cloud identity, or retain their existing vaults and improve rotation. The sensible comparison is which approach covers the actual estate with an acceptable operating burden.
The open-source option is particularly revealing. SPIRE is a production-ready implementation, not a mere research sketch. A capable platform team can build on it. Defakto has to earn its subscription by making the management, integration, and governance work easier. Open standards make that comparison possible; they do not automatically settle it in the vendor’s favour.
The money buys a wider brief
In October 2025, SPIRL introduced the Defakto name. The launch message expanded the story from workload identity into a fuller non-human IAM platform covering discovery, governance, issuance, and AI agents. The naming change accompanied an enlargement of the commercial brief.
Led by XYZ Venture Capital. Announced uses: product development and go-to-market expansion.
The funding announcement included continued participation from The General Partnership, Bloomberg Beta, WndrCo, Michael Coates, Adverb Ventures, and J.P. Morgan. Capital gives the company room to deepen its product and reach more buyers. It also raises the practical question that accompanies a wider platform: how well does each part work in a customer’s particular environment?
The commercial model is an enterprise subscription. A useful buying calculation includes the subscription, deployment work, ongoing operations, and the manual credential work it replaces. A procurement team should measure those costs against its own baseline. Capital raised by the vendor is a different number from the cost of running the product.
A machine passport needs a border policy
The documentation supplies a welcome dose of operational specificity. Defakto supports hosted and self-hosted trust domain servers. The documented self-hosted option deploys on Kubernetes using Helm and requires a registered organization, an authenticated command-line tool, configured agents, and connectivity to Defakto’s control plane.
For a team evaluating the approach, a contained pilot is a reasonable starting point: choose one pipeline or service, identify its owner and dependencies, and replace one stored credential. Check identity issuance, renewal, denied requests, and logs. Compare the operational effort before broadening the migration. That is an editorial recommendation drawn from the architecture, rather than a claimed customer recipe.
The conditions matter. A target service must accept the relevant identity or federation mechanism. Runtime evidence must be trustworthy. Policies must be narrow enough to be useful. An isolated environment unable to reach the documented endpoints needs an architecture discussion before deployment. Short credential lifetimes also make reliable issuance and renewal part of the operating job.
AI adds another boundary. Mind addresses identity and access for agents; authentication cannot establish that an agent’s proposed action is sensible. An authenticated agent can still make a poor decision within its permissions. Scope, delegation, oversight, and application safeguards remain consequential.
“Enterprises today can’t enter the age of AI on a foundation of static secrets and overprivileged access.”Eli Nesterov · Co-founder and CTO · October 2025
The next secret is an OAuth client secret
Recent work shows where the company is taking the idea. In June 2026, its VP of Open Standards, Pieter Kasselman, described a draft for authenticating OAuth clients with SPIFFE credentials and a joint Identiverse session with Cisco’s Nancy Cam-Winget. The proposal applies an existing workload identity to another place that commonly uses a shared secret.
Defakto’s careers page describes a fully remote, async-first organization with flexible hours, development budgets, and an emphasis on ownership and customers. It is a fitting operating posture for a company selling infrastructure that crosses environments. The more telling measure, however, will be what customers can remove: a key from a file, a standing permission from an account, an avoidable rotation chore from an engineer’s week.
That is the appealingly concrete ambition behind the company’s larger language. A machine should be able to prove where it came from, get the access its work requires, and finish without leaving a reusable admission ticket behind.
Explore the machinery
Defakto website ↗ · Platform tour ↗ · Request a demo ↗ · Technical documentation ↗
LinkedIn ↗ · X ↗ · Instagram ↗ · Facebook ↗ · GitHub ↗
Company news and essays ↗ · OAuth + SPIFFE ↗ · Series B announcement ↗