Robbie O’Brien knows that a technology business can disappear. One of his own failed in the dotcom crash of 2001. Years later, after building MetaCompliance and handing its leadership to a successor, he returned to that experience in his writing. Failure had taught him something about resilience that success alone could not. A business owner discussing cyber risk, he suggests, ought to understand what losing a business actually means.
That gives his present work an unusually personal starting point. O’Brien, the Derry-born technology founder known publicly as The Cybersecurity CEO, spends his time asking other leaders to take responsibility for the organisations they run. He co-founded Safe Harbour Security, a consultancy for smaller businesses, and hosts conversations about security and leadership. He has spent years selling the importance of paying attention. Now much of his attention is directed at the people who control the budget.
A long apprenticeship in getting people to listen
Before MetaCompliance, O’Brien worked for Capita and Intergraph Corporation. His career included developing and exiting three technology businesses before the period in which he was scaling the security company. He was also an Ernst & Young Entrepreneur of the Year finalist. Those experiences placed him on both sides of an awkward conversation: the specialist explaining a risk, and the executive deciding what deserves scarce time and money.
He founded MetaCompliance in 2005. Its subject was the human side of cybersecurity: whether people understood the risks in their working day, whether they followed policies, and whether an organisation could demonstrate that they had. Selling that idea required more than an explanation of the software. It required persuading customers that what employees did belonged on the security agenda.
By 2014, O’Brien was writing about the danger of an information security programme becoming a “minority sport”. A project could have its paperwork in order and still fail to involve the people whose actions mattered. He argued for a year-long programme, tailored messages for high-risk roles, and executive backing. It was an early version of the argument that would follow him through the next decade: a launch date is a beginning, and participation has to survive it.
“It has helped me scale myself.”
Robbie O’Brien, on Tenzing’s Sherpa programme
The founder needed a bigger team, too
In January 2021, MetaCompliance took investment from Tenzing. The business had 110 employees and served more than 900 organisations across public and private sectors. Customers were in the UK, Europe and further afield. There was already a substantial company to work with; O’Brien and his management team wanted help expanding it.
The management team stayed in their roles and invested again as shareholders. Tenzing brought growth experience as well as capital, with Gareth Healy and Milan Kellner joining the board. For a founder, that arrangement carried a practical question: how much more could the organisation accomplish with people who had helped other companies through the same stage?
Two measures of MetaCompliance when O’Brien and the management team partnered with Tenzing.
O’Brien later described the partnership using a runner’s comparison: someone practising alone gets a coach and discovers another gear. Tenzing’s account of the business describes a management team that had bootstrapped its growth, considered a trade sale, and decided there was more to build. Localisation and cultural fit mattered because employee training had to work for audiences in different countries.
One particularly revealing detail is his enthusiasm for Tenzing’s Sherpa programme, which places commercially minded operators alongside portfolio CEOs. O’Brien valued having another capable person tackle projects that neither he nor his existing team could reach. The founder selling employee engagement had his own very ordinary management problem: more worthwhile work than hours available. Extra hands gave him room to act.
Expansion acquired a geographical shape. In June 2022, MetaCompliance bought Copenhagen-based MOCH, its first acquisition. MOCH’s founders, Morten Ørsted and Christian Ravn, brought a business specialising in digital learning and compliance. O’Brien described the purchase as adding European capacity and capability. A company concerned with how people learn was growing partly by bringing another learning business into the fold.
The trouble with sending everyone the same lesson
O’Brien’s arguments about training become more interesting when he gets specific. Consider a human resources team. Security advice may discourage opening attachments, yet the department’s daily work can involve receiving CVs from unfamiliar email addresses. The advice and the job collide. Telling people to be careful leaves that collision unresolved.
His answer is to understand the role before writing the lesson. In a discussion of personalisation, he contrasted generic cybersecurity language with the concerns of people working on a production line or in a power plant. The safety of their machinery makes sense to them immediately. The vocabulary needs to meet the work. Even the version of Spanish used in training matters when the audience spans Europe and South America.
In his own 2023 writing, he also considered where employees wanted to receive material, from Microsoft Teams to learning systems and branded apps. Finance teams should see risks expressed through their own policies and working language. Quizzes, simulations and engagement measures could help establish whether an approach was connecting. The practical question was whether somebody would recognise a lesson when the relevant moment arrived.
There is room for amusement in this work. In a 2021 conversation with Jenny Radcliffe on Human Factor Security, O’Brien discussed personality and humour in training, alongside his objection to exercises completed merely to tick a box. A lesson still has to earn attention. The annual training module competes with every other task on an employee’s screen, and its claim on their time needs to be convincing.
Passing on the title
Recognition arrived during the building years. In 2019, O’Brien received the IT category’s Most Influential CEO of the Year award at the CV Corporate Excellence Awards. His response credited the team’s work on automation and training. The next year, MetaCompliance’s scholarship contest asked students to identify the three cybersecurity threats facing Generation Z. Hasan Khanani, a mechanical engineering student at Birmingham, won £1,000 after entries from more than 20 universities.
O’Brien’s interest in making the subject accessible also reached print. He was a credited author of the 2020 Cyber Security Awareness For Dummies, MetaCompliance Special Edition, alongside cyber security editor Geraldine Strawbridge. Software, training, a student essay competition and a plain-language book were different routes into the same difficult territory: helping people see why security concerned them.
On 3 October 2023, James Mackay succeeded him as CEO. Mackay had spent seven years at MetaCompliance and was its chief operating officer. O’Brien moved into the chief evangelist role, initially remaining on the board. He would concentrate on speaking with customers, industry leaders and others about personalised security awareness.
The transition came with the business still growing. For the year ending March 2023, MetaCompliance reported revenue of £16.6 million, up 32%, and pre-tax profit of £5.1 million, up 39%. Those are company figures, rather than a measure of the founder’s personal wealth. They describe the operating business he was handing on.
- 2005Founds MetaCompliance
- 2021Partners with Tenzing
- 2023Hands the CEO role to James Mackay
- 2025Announces his departure
In March 2025, O’Brien announced that he had stepped away altogether. He described a transition planned 18 months earlier with Tenzing’s Guy Gillon and Milan Kellner. His next interests were business scaling and cybersecurity, with a particular focus on helping founders and CEOs as an investor and hands-on adviser. Operational technology and smaller businesses were areas he wanted to support.
A local photograph with a wider story
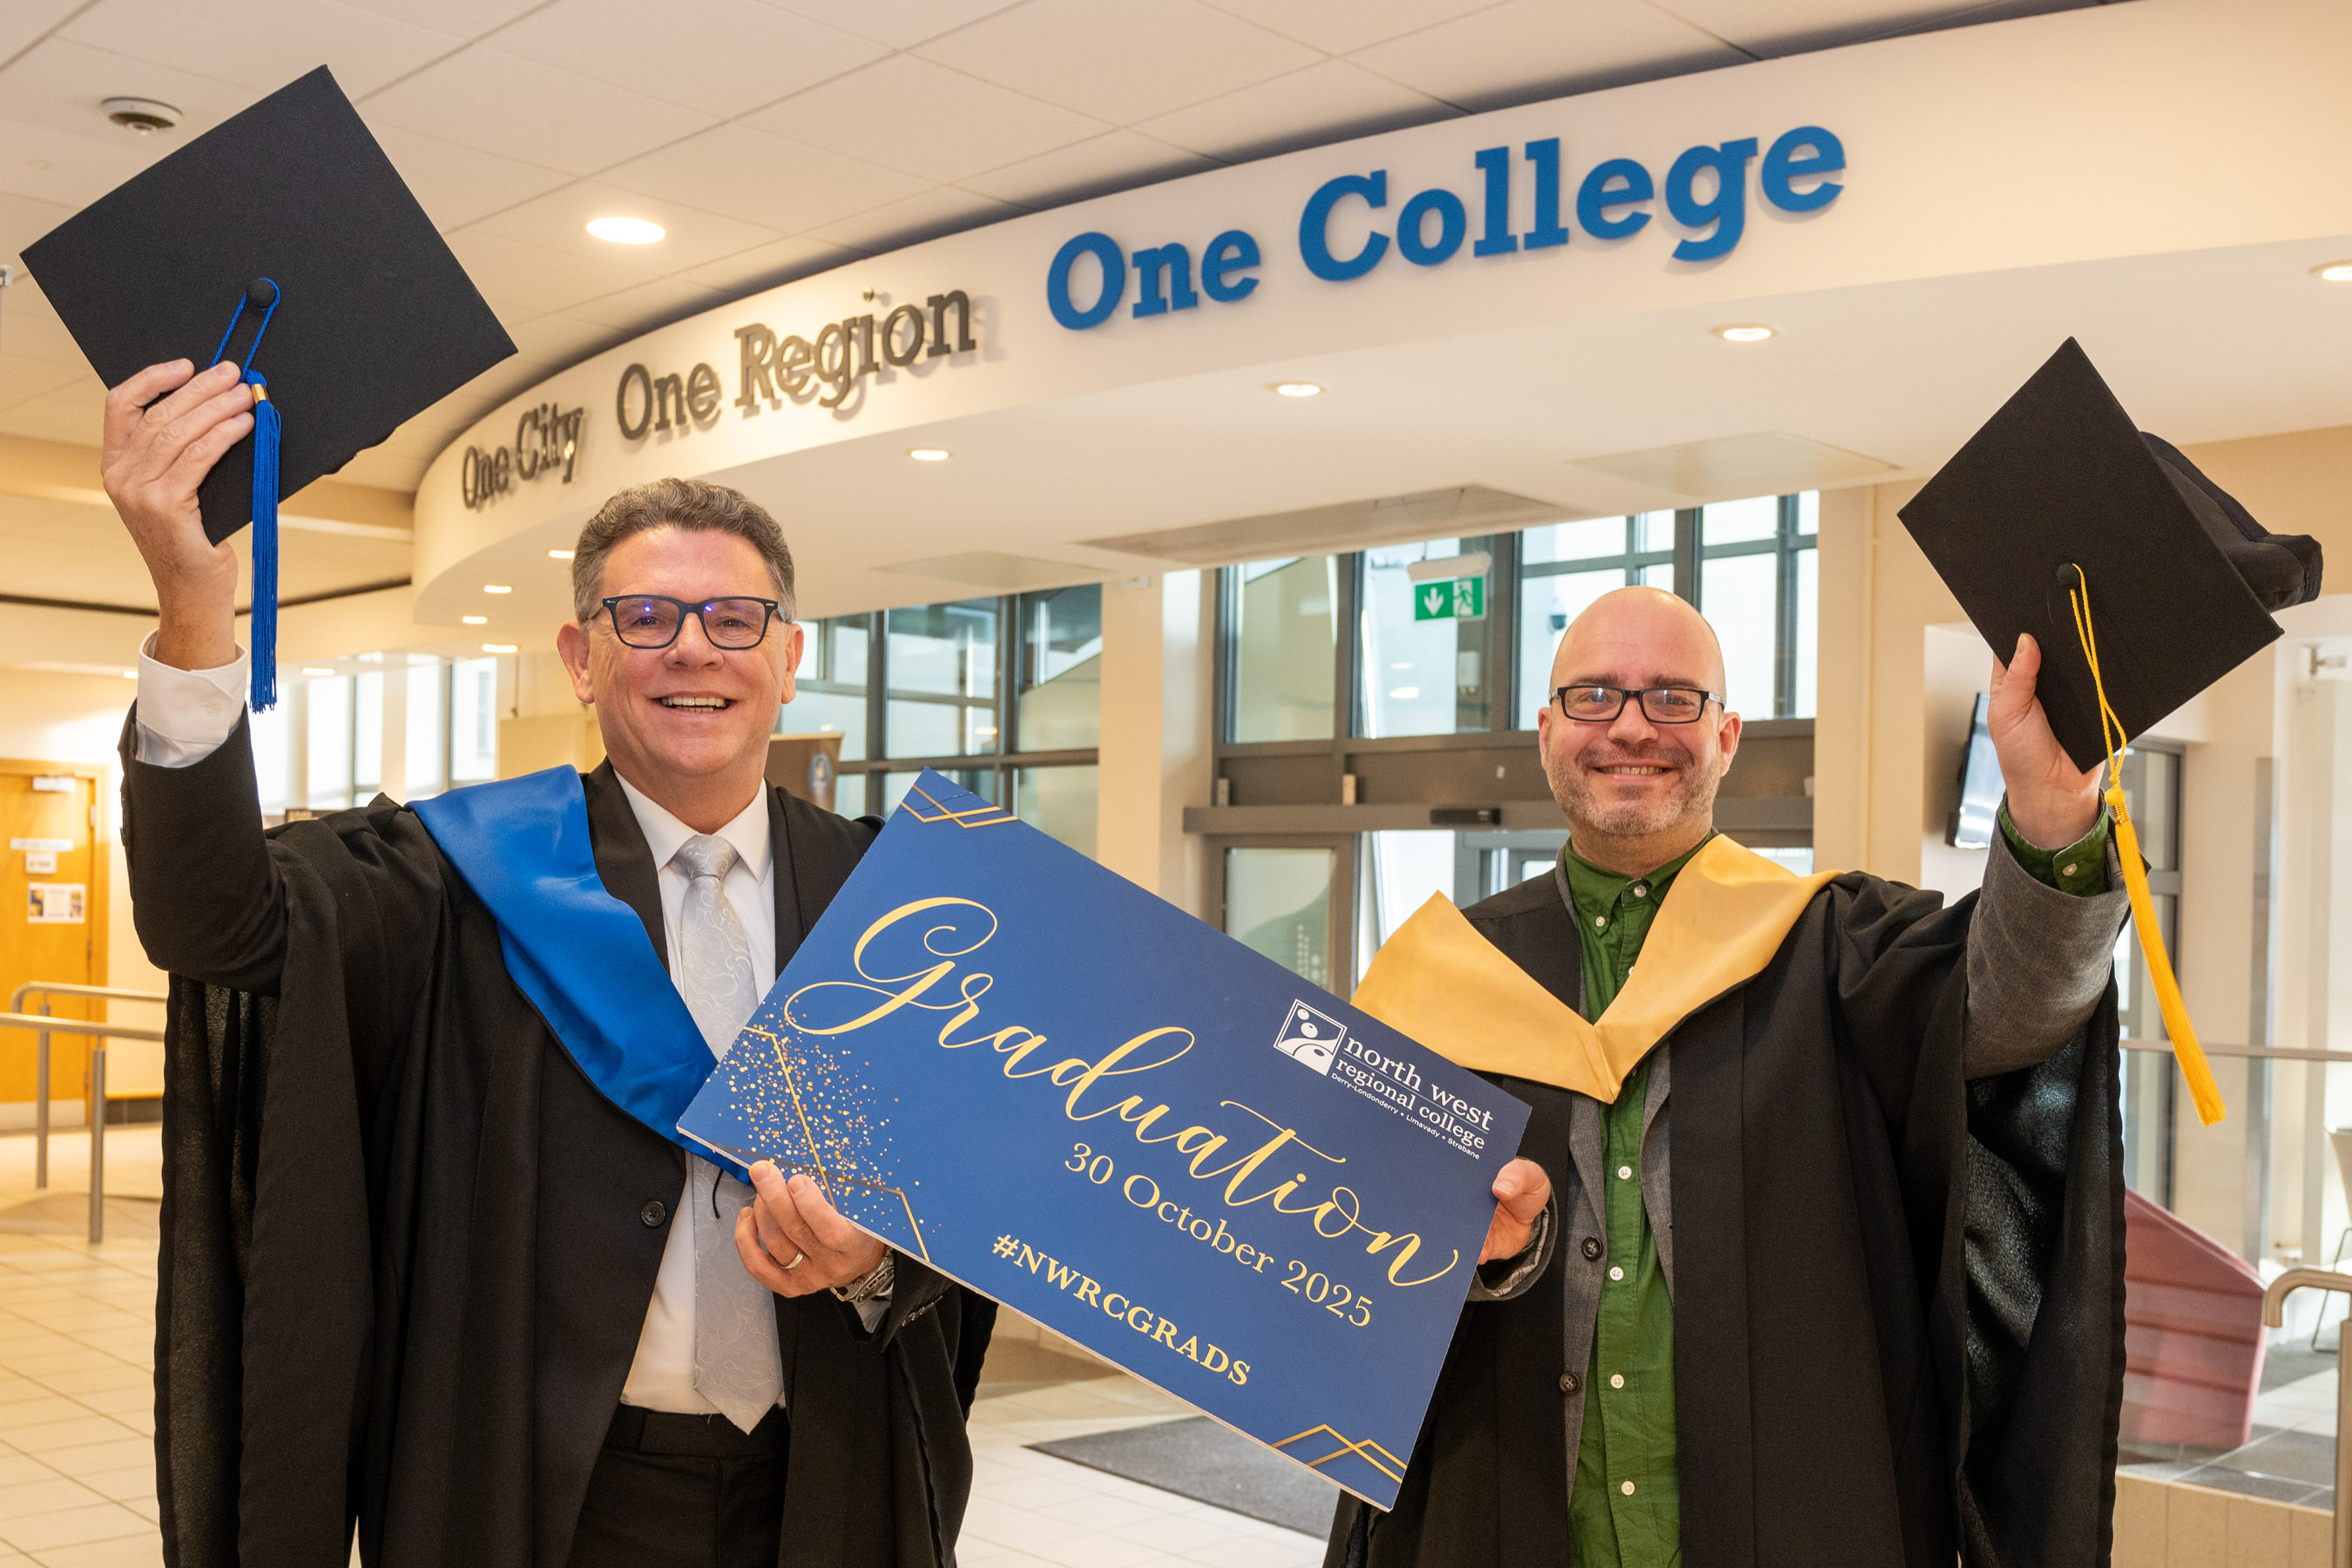
That October, North West Regional College recognised his contribution to the economy with an honorary award. He shared the occasion with Alastair Cameron, founder of the Derry technology conference TechTides. The college celebrated O’Brien as someone born and raised in the city whose businesses had created jobs and carried its capabilities into international markets.
The photograph has its own modest pleasures: academic robes, broad smiles and mortarboards held aloft. After the acquisitions, investment announcements and changes of title, here was a different sort of milestone. The place where he grew up was recognising the work. For a career spent explaining remote digital risks, the acknowledgement was pleasingly close to home.
Smaller businesses, the same uncomfortable question
At Safe Harbour Security, O’Brien is co-founder and chairman. The consultancy addresses the gap between the security resources available to large enterprises and those within reach of smaller organisations. Its services include penetration testing, risk advice, policy work, training and access to a virtual security manager. It operates from Derry, Dublin and London, serving businesses across the UK and Ireland.
In February 2026, he warned that AI was making fraudulent approaches more convincing and easier to produce at volume. The familiar reassurance that a scam would betray itself through clumsy language was wearing thin. He and the Safe Harbour team promoted briefings for business leaders who needed practical steps without the resources of an enterprise security department.
His own podcast carries the discussion into longer conversations. Guests have included Jane Frankland, Martin Smith and Steve Lorimer. With Lorimer, a former MetaCompliance customer responsible for security and privacy at Hexagon, O’Brien explored the meaning of putting security first, including disagreements about where cybersecurity should report. The conversation allowed room for an experienced guest to push back.
He is also working on a book for senior leaders and is listed to speak at the European Digital Governance Summit in November 2026. Across those projects, the audience is increasingly explicit: CEOs and boards. The founder who once tried to get employees to pay attention is asking their bosses to do the same. He has already experienced a business ending. There is a reason he keeps asking what it takes for one to continue.
Keep following the conversation
The latest writing, the longer conversations and the company he now chairs.