The course is finished. The box is ticked. Somewhere in the inbox, a plausible-looking message is waiting to find out whether any of it stuck. That gap between completing security training and making a good decision is the territory MetaCompliance wants to own.
The company sells organisations a way to teach employees, rehearse attacks and keep the resulting paperwork in order. Its audience is familiar: the security manager trying to reach busy colleagues, the compliance officer chasing acknowledgements, the executive who wants evidence that the programme is doing something. The pitch joins those jobs together.
That makes MetaCompliance an interesting business to watch. It sits where workplace education meets security software, with a growing appetite for behavioural data. Its commercial challenge is to make a recurring administrative obligation useful enough that customers want more of it.
The induction email had done its shift
At Energia Group, the starting point was ordinary. The energy business used employee inductions and internal communications to deliver security awareness. It concluded that a fuller training programme would do the job better. In its published customer account, Energia describes adopting MetaCompliance to deliver courses and run phishing tests.
The change included a browser-accessible platform and links from the company intranet. Videos, quizzes and simulated phishing supplied different ways to engage staff. Reporting replaced the manual collection of results. These are modest operational details, but they explain the purchase more clearly than a promise to transform security culture.
Energia also reported that awareness training became a regular item on its Risk Management Committee agenda and part of its board-approved security strategy. The account describes staff becoming more questioning about incoming email. That is a customer’s assessment, rather than a controlled measurement of prevented breaches. Still, it identifies what the organisation wanted to change: the programme’s reach, its administration and its place in management discussion.
A programme has to come back around. Diagram illustrates the product approach, not measured customer results.
Practice, with a paper trail
MetaCompliance’s phishing simulations let administrators tailor scenarios by role, department or location. Feedback gives employees a chance to learn from the exercise, while reporting tracks clicks, reports and trends. A finance team and a public-facing service desk can face different examples without the organisation building separate programmes from scratch.
The education side includes short videos, scenarios and Cyber Police, a story-led training format. Fusion and Virtual Presenter support personalised content. The company advertises training in more than 40 languages, delivery through Microsoft Teams and SCORM export to existing learning-management systems. Its training description makes localisation and distribution part of the product, alongside the lessons themselves.
That combination matters in a dispersed organisation. A well-written course still needs the right audience, a comprehensible voice and a route onto the employee’s screen. The interpretation here is straightforward: much of the product’s usefulness rests on removing small obstacles between assigning training and actually receiving it.
Policy management adds another reason to stay in the system. MetaCompliance tracks acknowledgements and evidence of understanding, while its broader compliance offering includes privacy and incident management. Its compliance tools connect employee participation with records that administrators can retrieve later.
The demand predates today’s human-risk language. In 2014, Scottish law firm Harper Macleod adopted the policy software to distribute information, capture staff sign-off and demonstrate its risk-management arrangements. For a professional-services firm, the product was partly about being able to show the work. A policy sitting unread in a folder is a poor witness.
When the next lesson starts with a breach
The sharper development came in February 2026. MetaCompliance launched Exposure Monitoring, which checks employee email addresses against verified breach data. When exposure appears, the system alerts security teams and assigns affected users short response-focused learning. The exposure also contributes to the employee’s human-risk score.
The launch announcement included Power BI integration, Slack messaging and custom deepfake content. It also named Ionbond as an Exposure Monitoring customer. The product direction is clear: training assignments can begin with an observed exposure, giving the next lesson a specific reason to exist.
That changes the usefulness of the dashboard, provided somebody acts on it. An exposed email address is a signal to investigate; it does not establish that a particular employee caused a breach. Similarly, a risk score is a prioritisation tool. Treating either as a verdict would ask the software to settle questions its inputs cannot answer.
MetaCompliance’s analytics offering groups information about individuals and teams, supports campaign reports and allows data export. For a buyer, the sensible demonstration is a complete journey: show the signal, show the assignment, show the response and then show how the team decides what to do next.
The invoice has more than one line
MetaCompliance earns money through business subscriptions, with optional managed services, professional work and customised services. Its commercial terms also distinguish standard support from enhanced provision. Buying access and buying help to run a programme are separate purchasing decisions.
One concrete price appears in the UK government’s G-Cloud 14 marketplace: MetaPolicy is listed at £24.99 per user per year. Multiplying that by 500 users gives £12,495 annually at the listed rate. That arithmetic describes one policy-management module, before considering applicable taxes or other contracted services.
A scope check belongs beside every price check. Illustration uses the G-Cloud 14 rate for MetaPolicy alone.
The other expense is attention. Somebody must choose audiences, approve content and review what the reports mean. Automation can reduce reminders and repetitive administration. It cannot supply management interest. An organisation buying a training library for occasional use should weigh a different set of benefits from one trying to coordinate policies, rehearsals and follow-up across several countries.
There is competition for both budgets. KnowBe4 also sells personalised training, simulations and reinforcement. MetaCompliance’s case therefore rests on how its content, compliance workflows, localisation and support fit together for a particular customer. The phrase “human risk management” alone does little to distinguish the vendors.
Growth needed an extra pair of hands
Robbie O’Brien founded MetaCompliance in 2005. When Tenzing invested in January 2021, the company reported 110 employees and more than 900 customer organisations. Management chose the investor partly for its experience growing similar businesses. The founder’s decision was about access to expertise as well as money.
Expansion followed through product development and acquisitions. MetaCompliance bought Copenhagen-based MOCH in 2022, adding a Danish operation with digital-learning experience. Increase Your Skills added German reach in 2023. These transactions brought local teams into a business selling training across languages and workplace cultures.
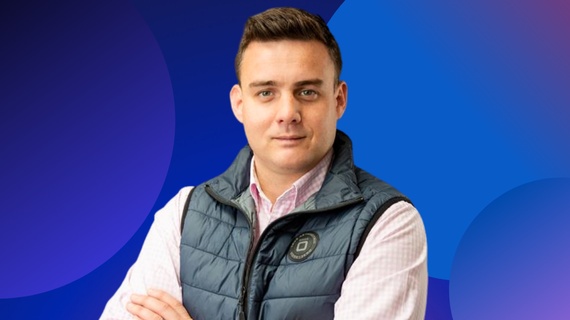
Acquisitions also consumed management time. In a Tenzing account published in January 2026, operator Miles MacInnes described a senior team handling rapid growth, exit preparations and a German acquisition. His brief was to lead integration, working with the CEO and CFO and coordinating teams on the ground.
“The business was growing fast, and the senior team was stretched.”Miles MacInnes · Tenzing account, January 2026
The transferable lesson is specific: assign integration work to someone with the time and authority to do it. Adding an acquisition to an already full executive calendar does not create capacity. Here, the investor’s embedded operator supplied it.
In December 2024, Keensight announced an agreement to acquire a majority stake. Tenzing’s exit announcement reported a 5.5x return on invested capital, with completion then expected in the new year. It credited investment in sales, inbound marketing, Portuguese development capacity and European acquisitions. The return measures the investor’s outcome, rather than a customer’s security improvement.
Under Keensight’s backing, MetaCompliance acquired Junglemap in December 2025. The Nordic company brought approximately 1,200 customers and NanoLearning, an approach built around short, targeted lessons. The attraction included a teaching method and established regional relationships. MetaCompliance reported more than six million users worldwide that month.
The workday is the test
The 2026 release log brings the story back to employees’ screens. July added integration with Outlook’s native Report Phishing button. August brought Teams notifications within campaigns, AI-content labels and upgraded Virtual Presenter avatars. These product updates concentrate on how people encounter training, recognise generated material and send a suspicious message to the security team.
The company’s own workplace also has an external marker. B Lab records B Corp certification from July 2025, with an impact score of 90.8. Its careers page advertises healthcare, enhanced family leave and pension matching up to 8%. Those details concern corporate practices; they answer a different question from whether a phishing exercise works.
For a prospective customer, the useful test is similarly concrete. Pick a real department, a relevant scenario and a follow-up action before judging the dashboard. Look at participation and reporting together. Ask whether administrators can maintain the programme, and whether staff have a practical way to respond when something looks wrong.
MetaCompliance’s opportunity lives in that ordinary working day. The suspicious message arrives between other tasks. The policy competes with a deadline. The training has to earn enough attention to influence the next decision. A completion certificate marks the end of a course. For this business, the interesting part comes afterwards.