security-founder
(5)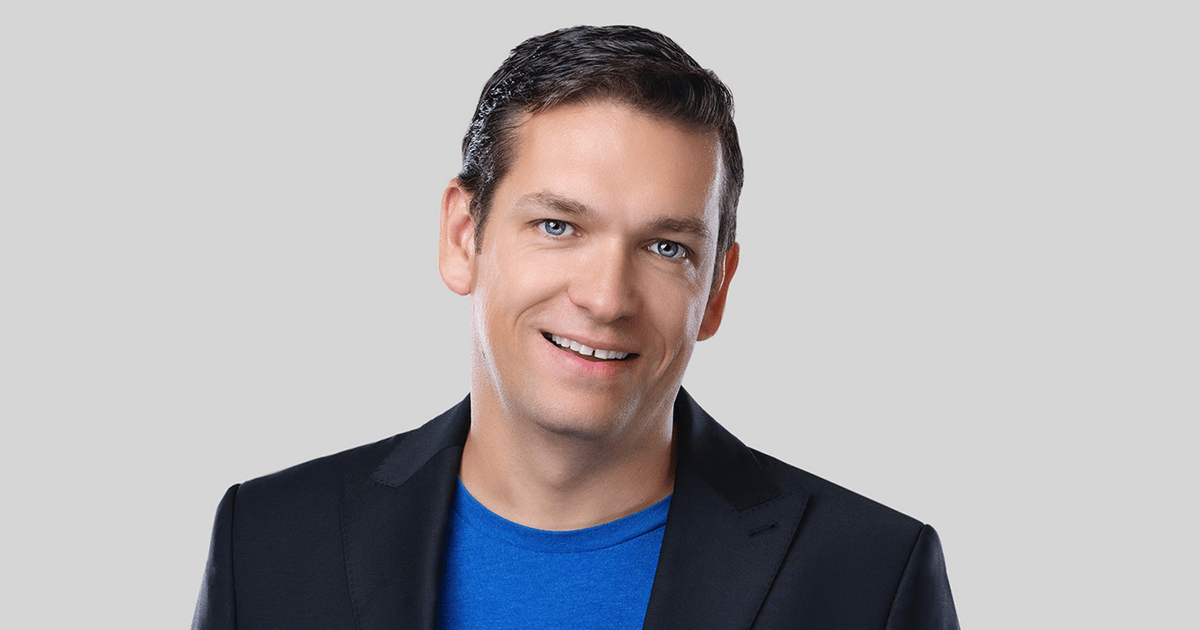
Danny Jenkins Built a Security Company Around One Unfashionable Word: No
He left school for computers, learned to think like an attacker, and bet the grocery money on a simple defense: decide what is allowed, then refuse everything else.
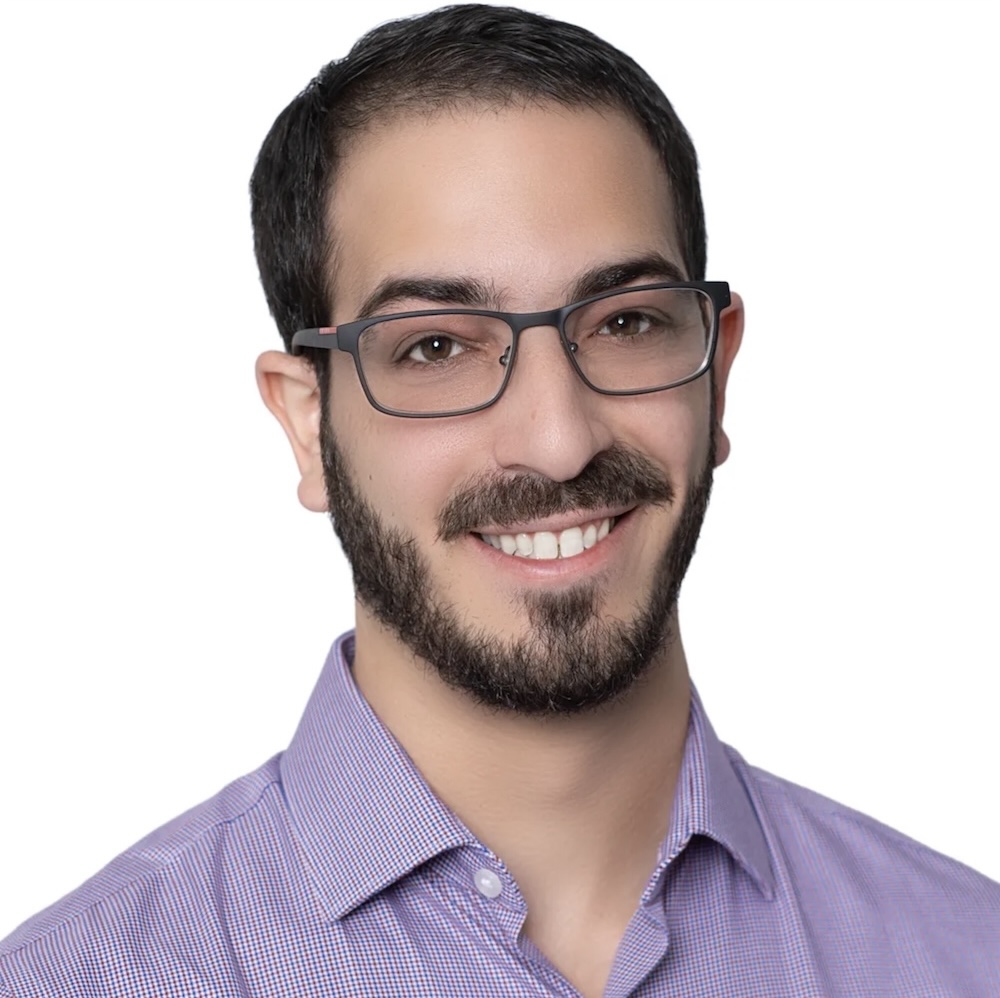
Rob Gurzeev Built a Security Company Around the Things Nobody Knows They Own
From teenage IRC channels to Unit 8200 and a Tel Aviv balcony, Rob Gurzeev kept returning to one stubborn idea: the dangerous asset is often the one a company forgot it had.
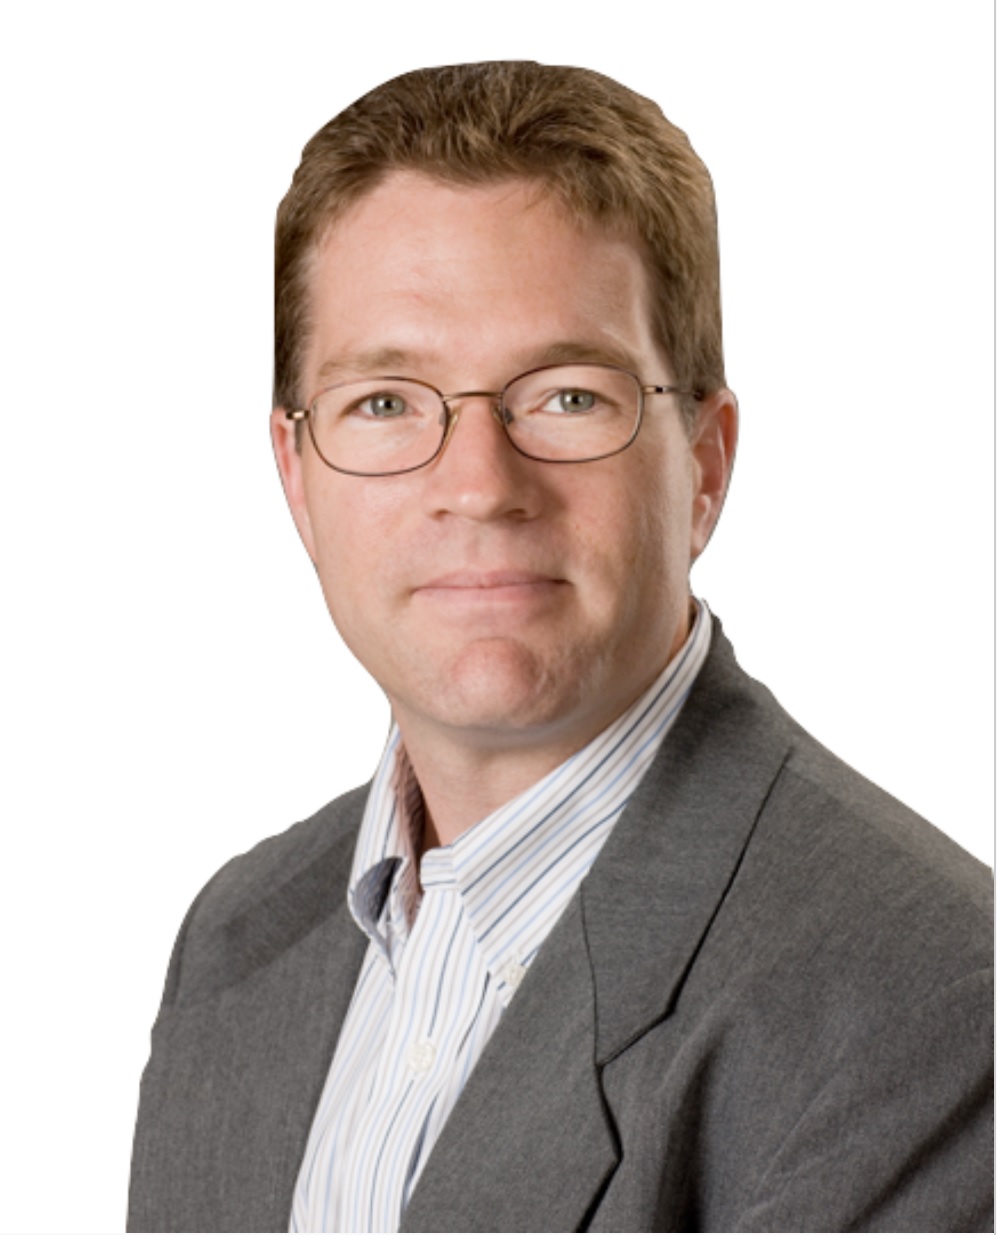
Brendan Hannigan Keeps Finding the Door Everyone Left Open
From a compulsory FORTRAN class in Dublin to Q1 Labs, IBM Security and Sonrai, Brendan Hannigan has spent a career making invisible access visible. His latest wager is simple: the cloud gets safer when unused permission is removed before an attacker can borrow it.
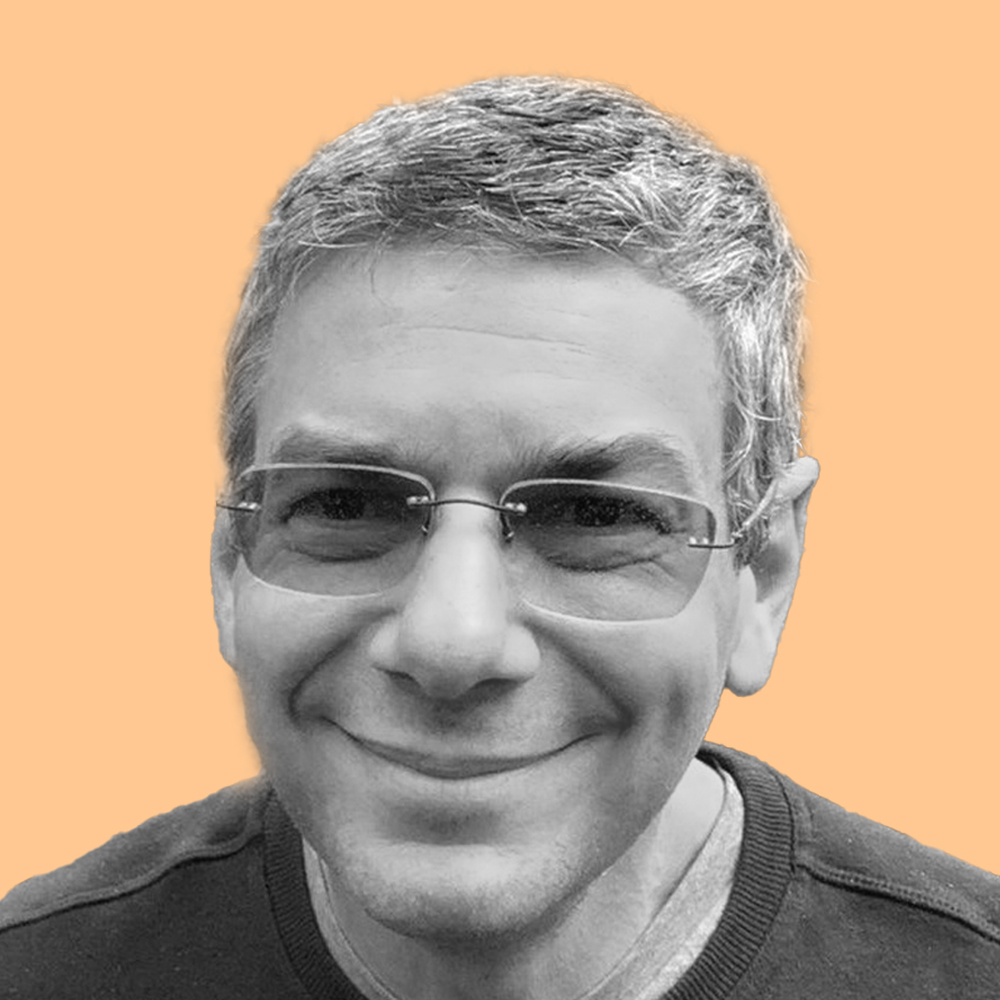
David Goldschlag Is Giving Machines Their Own ID Check
He helped invent onion routing, built and sold two security companies, and now wants applications and AI agents to stop borrowing human credentials. The through-line is a career spent replacing assumed trust with evidence.
Lior Yaari Is Building Security for the Software Nobody Approved
Employees can adopt a new app before IT finishes its first coffee. Grip Security's co-founder wants to preserve that speed while giving security teams a map, a set of controls, and fewer nasty surprises.