The troublesome invoice might arrive with perfectly respectable credentials. Imagine an employee who can add a supplier in one business application and approve its payment in another. Each permission has an explanation. Put them together, however, and a company has handed one person both sides of a transaction. The login succeeds. The control question has only just begun.
- The job: connect application access, business activity, and audit evidence.
- The buyers: enterprises managing complicated ERP systems and compliance obligations.
- The useful distinction: separate a risky permission from a risky action.
Pathlock occupies this rather consequential space between permission and action. Its software helps organizations manage who gets access, check combinations of privileges, monitor transactions, and assemble evidence for auditors. SAP, Oracle, Workday, and PeopleSoft are part of its territory. The company advertises pre-built connectors for more than 150 applications. The important word is applications: the places where a business actually orders, pays, hires, and records.
The invoice is the interesting part
In security language, our supplier example concerns segregation of duties, usually shortened to SoD. The principle is straightforward: divide sensitive work so one actor cannot quietly complete a dangerous sequence alone. The difficulty is translating that principle into the roles, authorization objects, fields, and transactions of different software systems.
Pathlock’s application access governance tools analyze those combinations and support access reviews, provisioning, and temporary elevated access. Continuous controls monitoring adds another layer: examining business activity after permissions have been granted. Its cybersecurity products address ERP vulnerabilities, threats, and the movement of software changes into production. These are related jobs, but buying one capability does not magically finish the others.
Jabil provides a useful example. In Pathlock’s published customer account, the manufacturer’s governance team was dealing with millions of daily SAP transactions and too much uncertainty about which conflicts mattered. Broad warnings consumed attention. Transaction details supplied something more actionable: who executed the conflicting activity, which invoice was involved, and whether the counterparty was a customer or vendor.
The attraction is easy to understand. A permission list describes possibilities. An invoice gives an investigator something to examine. Pathlock reports faster, more focused compliance work at Jabil; that account is customer testimony published by the seller, rather than an independent performance test. Still, the problem it describes is specific: the first bottleneck was interpretation.
A queue of forms, two people
At Lee County Schools, the bottleneck looked less like a risk dashboard and more like a crowded inbox. Pathlock’s case study describes two staff members handling access changes arriving through tickets, email, paper, and conversation. Daily requests reached 40-50. The district needed automated business-role assignments and job-specific PeopleSoft scripts.
“If HR puts someone into the system in the morning, they’ve got access by the afternoon.”
Charles Lukes / PeopleSoft Security Administrator, Lee County Schools
The implementation checks for new hires and job changes every three hours, then applies access and launches the relevant scripts. The published result: fewer than ten request forms per day. What made automation useful was the connection between an HR event and the actual work needed inside PeopleSoft.
A company assembled around the problem
Anand Adya founded the business as Greenlight Technologies in 2004. In March 2021 it became Pathlock alongside a $20 million strategic investment from Vertica Capital Partners. The name change accompanied a broader ambition: govern access across enterprise applications as businesses adopted more cloud software.
The next year brought a more substantial rearrangement. Pathlock combined with Appsian and Security Weaver, while CSI Tools and SAST Solutions joined the group. A $200 million capital announcement supported the combination and growth. Appsian contributed ERP data-security capabilities; Security Weaver brought SAP access-risk and role-design expertise. The logic was to put adjacent controls under one roof.
This history helps explain Pathlock’s market position. It competes in territory also served by Saviynt, SailPoint, and SAP access-control products, with different overlaps depending on the assignment. Pathlock emphasizes detailed controls inside business applications. Its own comparison material also describes adding ERP controls alongside an existing identity-governance platform. Replacement is one commercial route; coexistence is another.
One workflow before the big rollout
The business model is enterprise software sold through subscriptions and negotiated contracts. Pathlock describes cloud pricing as typically tied to users and connected applications. For a buyer, the useful budget question is the total cost of connecting systems, configuring policy, running reviews, and maintaining the arrangement.
A sensible evaluation follows one sensitive process all the way through. Pick a payment workflow. Identify its owner, map the permissions, introduce a conflicting combination, and inspect the resulting evidence. Then measure the time required to investigate it. This is a practical inference from the customer stories: evaluate the work a team must finish, rather than the number of warnings a screen can display.
That approach requires usable identity data, understood business rules, and people responsible for exceptions. Automation will faithfully repeat a badly specified decision. A small organization with simple access needs may have little use for this much ERP specialization; customer identity management and unstructured-data governance can also require complementary tools.
The next user may be a machine
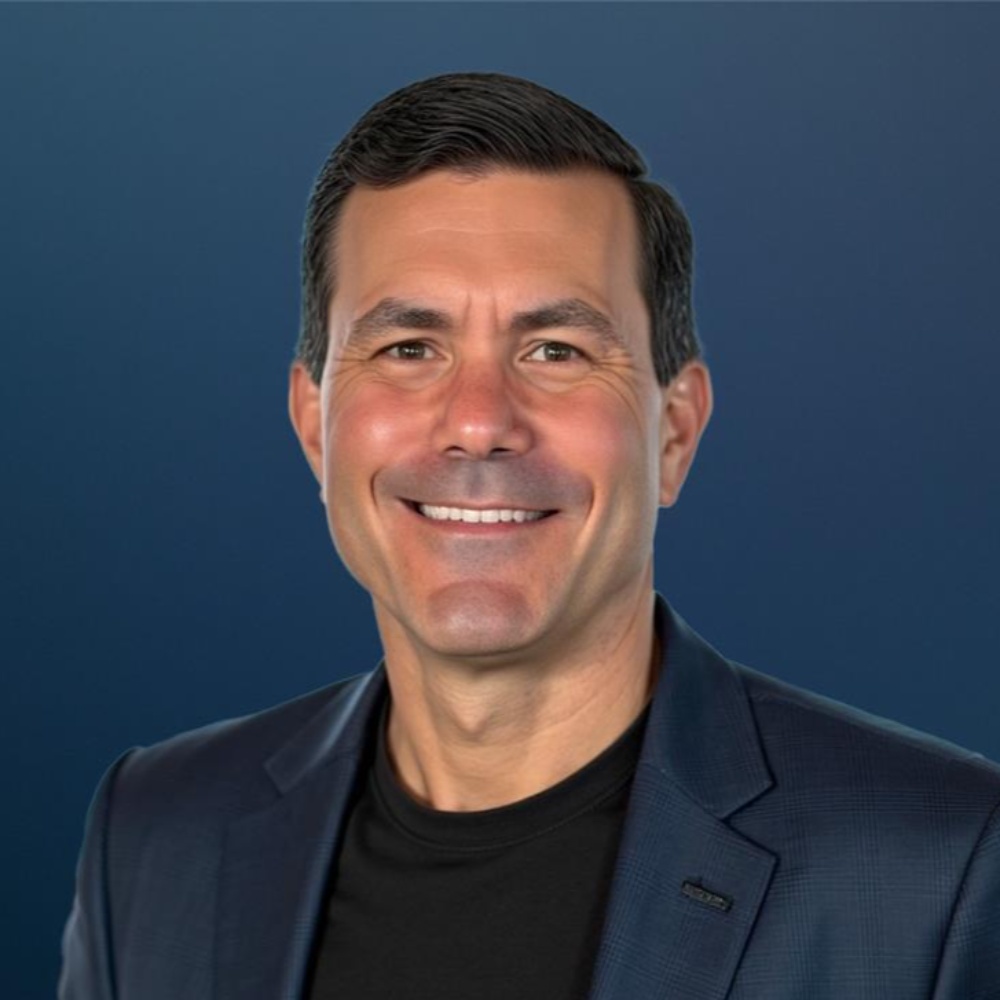
Damon Tompkins became CEO in January 2026, when Pathlock reported 1,400 enterprise customers. In June, the company introduced Nexus, bringing its transaction-first positioning to human users, service accounts, bots, and AI agents. An August alliance with KPMG added another route into enterprises modernizing core systems.
The machine changes the speed and volume of activity. The old accounting question survives: who can perform the action, who checks it, and what record remains? Pathlock’s proposition becomes clearest at that final step. A successful login begins a session. A business still needs to explain the payment.
Open the application door
Explore Pathlock, its Nexus platform, newsroom, and customer stories. Follow the company on LinkedIn or X.
Try the elevated-access product tour Watch the PeopleSoft analytics webinar