The most revealing thing about UpGuard is not a hacker story. It is a procurement story. At a company where security executive Nigel Hedges once worked, a multimillion-dollar contract failed due diligence. The deal had reached the moment when everyone expected a signature; instead, weak answers about a vendor's security stopped it. Hedges needed a way to inspect suppliers quickly, before the paperwork became theater. He tried UpGuard, later introduced it at other employers, and eventually brought it to Chemist Warehouse.
There, the old process was painfully familiar: spreadsheets, email threads, static questionnaires and repeated nudges. A vendor review could consume a month. With UpGuard, Chemist Warehouse says it brought that down to a week. The software did not abolish judgment. It reordered the work. An outside-in scan offered a first view of the vendor, adaptive questionnaires filled the evidence gaps, and reporting translated technical findings for executives. The company's security team reported a 75 percent reduction in assessment time.
The unsexy problem is the business
UpGuard sells enterprise cybersecurity software, but its enemy is administrative drag. Every sizable company depends on cloud platforms, payroll vendors, payment processors, contractors and specialist software. Each dependency creates a question: if that supplier is compromised, what reaches us? Traditional due diligence often answers with a long questionnaire at onboarding and another one next year. The answers may be sincere and still go stale the next morning.
UpGuard begins with non-intrusive, outside-in data. It maps internet-facing assets, looks for exposed services and risky configurations, follows threat feeds, finds leaked credentials and produces a security rating. The important move is pairing that measurement with workflow. A team can tier vendors, request documents, send questionnaires, identify failed controls, ask for remediation and monitor changes after approval. The score is the doorbell, not the whole conversation.
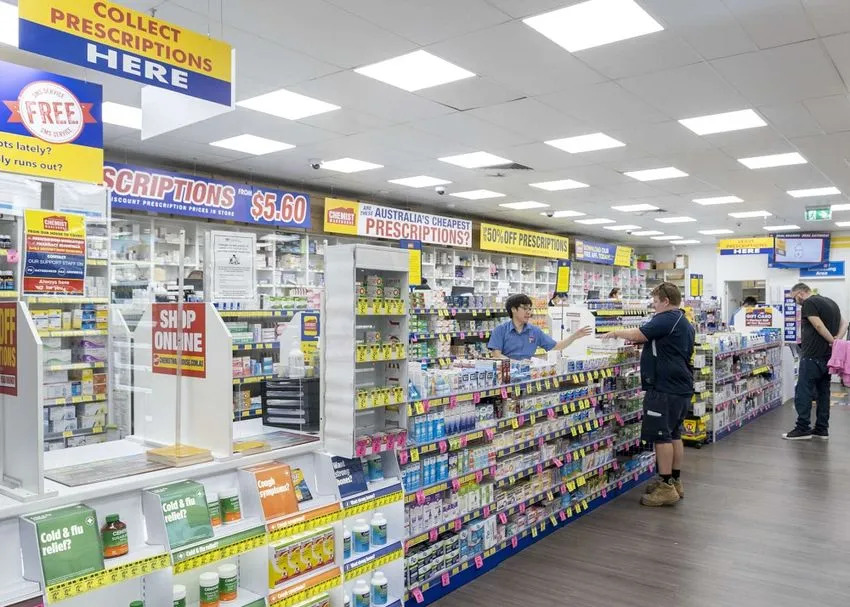
“Before UpGuard, everything was manual and ad hoc.”Andrew Morton, Head of IT GRC and Assurance, Chemist Warehouse
Five products, one operating loop
The company now describes its category as cyber risk posture management. The phrase is bulky, but the product map is legible. Vendor Risk covers suppliers and their suppliers. Breach Risk watches an organization's own attack surface, leaked data and external threats. Trust Exchange packages security evidence so a company can answer customer due diligence without starting from zero. User Risk maps shadow software, identity exposure and risky workforce behavior. Risk Automations connects the findings to systems such as Jira, ServiceNow, Slack, Okta and the major clouds.
This is where UpGuard separates itself from a pure ratings service. BitSight, SecurityScorecard, Black Kite and RiskRecon all compete in external risk intelligence. Panorays and Prevalent lean further into assessment workflows. OneTrust and ServiceNow approach the problem as part of broader governance software. UpGuard's position is that a lean team should not have to stitch together ratings, questionnaires, attack-surface monitoring, trust documents and routing. Its advantage, if the integrations hold up, is connective tissue.
The customer list makes the market boundary clearer. Morningstar, Mattress Firm, Tech Mahindra, Brightcove, St John WA and Colorado State University appear among its case studies. These organizations have little in common at first glance. One sells investment research, one mattresses, one technology services and one education. What they share is a sprawling dependency map. Money, health information, student records or business operations can pass through vendors the security team does not control. UpGuard is useful where procurement speed and security assurance are forced to share a calendar.
Some customers use only part of the machine. Mattress Firm has described continuously monitoring vendors through their life cycle. Tech Mahindra reported scanning supplier domains, watching ratings and triggering targeted remediation when risks appeared. A large Australian fund manager used UpGuard's managed service to handle outreach and evidence review, reportedly halving assessment time. That service matters because software does not make a reluctant vendor answer an email. UpGuard can supply people to chase the response, inspect the documents and return a summary to the customer's security team.
That also explains the company's AI pitch. UpGuard says models help read evidence, map controls, draft questionnaire responses, triage noisy signals and create plain-language summaries. By February 2026, it reported more than 70,000 AI risk assessments and 700,000 autofilled questionnaires. These are deliberately clerical applications of AI. The useful output is not synthetic wisdom; it is fewer hours spent finding a SOC 2 clause or proving that an alert belongs to somebody else.
What it costs - and what the buyer is comparing
UpGuard's public Standard Vendor Risk plan includes 50 monitored vendors. Additional vendors are listed at $79 a month. Larger tiers and much of the broader platform require a sales conversation.
That starting price is material for a small business and ordinary for enterprise security. The honest comparison is not software versus zero. It is software versus analyst time, review delays, a fragmented tool stack and the cost of approving the wrong vendor. Chemist Warehouse's month-to-week result gives buyers a useful equation: multiply the reviews completed in a year by the hours removed from each, then add the value of catching a bad dependency before contract signature.
UpGuard itself followed a patient expansion. Founded in 2012 as ScriptRock by Mike Baukes, Alan Sharp-Paul and Leo Venegas, it initially worked closer to configuration and operational assurance. A $17 million Series B in 2016 backed its move into cyber-risk benchmarking. Over the next decade, the company widened from vendor ratings to first-party exposure, reusable trust evidence, human risk and automation.
In February 2026, Springcoast Partners led a $75 million minority Series C. Existing backers include August Capital, Square Peg Capital and Pelion Venture Partners. UpGuard said the money would fund product development, global sales expansion and possible acquisitions. At the time, it reported more than 2,000 customers, a presence across 14 countries and more than 100 billion risk signals processed daily. Six months later, it arrived on Google Cloud Marketplace, making procurement easier for customers already committed to that cloud.
The company remains Australian at its center, with headquarters in Hobart, a U.S. base in Mountain View and a regional office in Sydney. Its distributed culture is unusually plainspoken for risk software. Published values include “Be excellent to each other,” “Pride in what we do,” and “Don't #!&$ the customer.” The phrasing is funny because it rejects the upholstered language of corporate values, but it also describes the hard part of this category: a rating provider can damage a vendor relationship if it treats a disputed finding as gospel. Listening, correction and explanation are product features here.
UpGuard also behaves partly like a research publisher. Its breach researchers have investigated exposed databases and data leaks, while its annual reports turn the company's scanning data into sector snapshots. In 2026, it reported on infostealer infections among ASX 200 companies, breaches among higher-education vendors and the time security teams lose gathering context. Research gives the brand authority and gives the product team a live catalog of ugly edge cases. It is also marketing with unusually useful raw material: show the hazard, quantify the wasted work, then demonstrate the workflow.
The conditions where it breaks
The central limitation is simple: the internet cannot reveal everything happening inside a company. Outside-in scanning can find exposed assets, weak certificates, leaked credentials and observable attack paths. It cannot, by itself, prove that an internal incident plan works, that privacy practices match policy, that a backup restores cleanly or that a supplier will remain solvent. Asset attribution can also be messy when infrastructure is shared. A rating should sharpen a question, not become an automatic verdict.
Do not copy the dashboard. Copy the discipline.
- It will not work well if nobody owns remediation after the alert arrives.
- It is incomplete for physical, financial, legal and operational supplier risks outside cyber.
- Automation saves little when vendor inventory is missing or every supplier is treated as equally critical.
- AI-assisted evidence still needs review when a decision is regulated, high-impact or ambiguous.
The portable lesson is to start smaller than a platform purchase. List the vendors that can touch sensitive data or stop revenue. Tier them by consequence. Gather outside-in evidence before sending a form. Ask only what remains unknown. Attach every material issue to an owner and due date. Recheck after the fix. A team can run that loop with simple tools before buying anything; software becomes valuable when volume makes the loop collapse.
There is another useful rule in the Chemist Warehouse story: move the review earlier. The prior failed deal was expensive because security discovered the problem near the finish line. A fast first scan does not replace diligence, but it can surface obvious trouble before legal, procurement and a business sponsor spend weeks negotiating. That is the reader's most practical copy. Put a lightweight security gate near the beginning, reserve deep evidence collection for critical suppliers, and let low-risk purchases move without pretending every browser extension deserves a board investigation.
UpGuard fits best when the organization has enough suppliers and public infrastructure to make continuous monitoring useful, but not enough security staff to babysit five disconnected products. Its customers span finance, healthcare, retail, education, technology and the public sector. Their shared problem is not ignorance of cyber risk. It is the distance between knowing and closing.
That is a sturdier pitch than promising perfect prediction. Security teams do not need a machine that declares a vendor safe forever. They need a current, explainable reason to approve, reject, escalate or fix something today. UpGuard's bet is that the winning cyber-risk platform will be judged less by the number of red dots it produces than by how many disappear for the right reason.