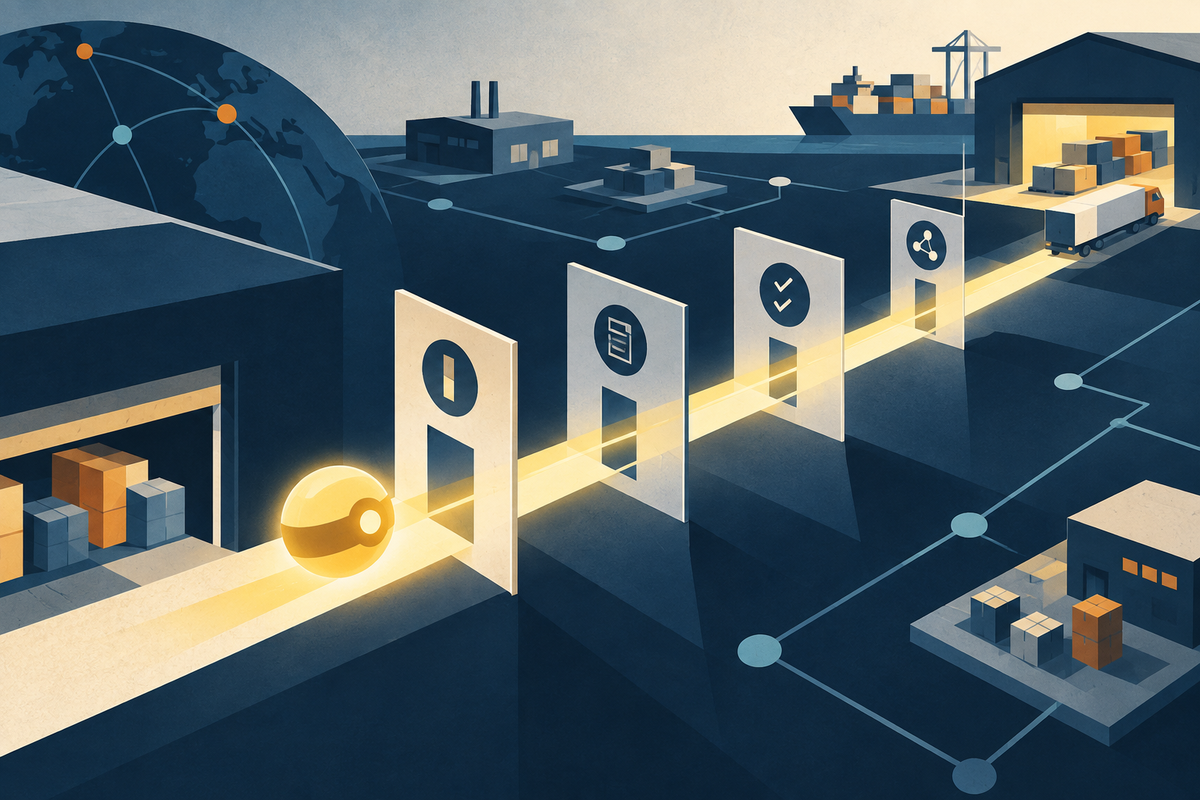
The next worker entering a freight operation may never carry a badge, complain about the coffee, or forget a password. It may retrieve rates, check customs documents, create shipments, update records, and coordinate work across several systems before a person finishes opening the morning queue. That speed is the attraction of agentic AI. It is also the source of the anxiety.
A chatbot offers an answer. An agent takes an action. In supply chains, the difference is physical and financial: an incorrect field can stall a load; an unauthorized promise can reset a customer’s expectations; an ill-timed system change can ripple through inventory, billing, and delivery. The important governance question is therefore not whether the software sounds intelligent. It is whether the business can say, with precision, who acted, what it touched, why it was allowed, and how to reconstruct the result.
Pallet’s answer is refreshingly unromantic. Do not invent a grand new constitution for machines. Extend the controls enterprises already use for employees, applications, and service accounts. Give every agent an identity. Limit its access to the workflow. Decide where it must stop. Record what it does. Control who can change the agent itself. The novelty is not in any single rule; it is in applying all five to software that can move work forward on its own.
The five-control stack
Who acts?
Where?
When stop?
What happened?
Who changes it?
Rule one: give the agent a badge
Identity is the beginning of accountability. Pallet argues that every agent should have distinct credentials, a named owner, and its own audit trail. That prevents the agent from disappearing inside a shared user account or inheriting a human operator’s broad access. It also lets security teams answer the first question after an exception: exactly which actor made the change?
Consider three agents working near one another. A quoting agent retrieves rates and drafts an offer. An import-documentation agent validates customs paperwork. An order-entry agent creates a shipment. They may touch some of the same records, but they are not interchangeable workers. Separate identities keep their histories, owners, and permissions legible. If one credential is compromised or one workflow starts behaving oddly, the company can isolate the actor rather than shut down the entire operation.
The practical move is simple: put agent identities into the same inventory used for other non-human accounts. Assign an accountable business owner and a technical owner. Set an expiration or review date. If nobody can explain what an identity is for, it should not retain access.
“The safest useful agent is not powerless. It is precisely empowered.”Yes Press
Rule two: permission follows the job
Traditional access control often begins with the user: what can this employee see and do? Agentic systems require a second lens: what does this specific workflow need in order to finish? Pallet calls for task-scoped, least-privileged permissions. The quoting agent can retrieve rates, consult pricing rules, and prepare a quote. It should not quietly gain the power to alter invoices, create orders, or rewrite customer records.
This distinction matters because agents cross software boundaries with unusual ease. The same workflow may open an email, read an attachment, query a transportation system, and update a system of record. Convenience can turn into permission creep unless every tool and action is tied to a narrow purpose. A good test is counterfactual: if the agent behaved perfectly but attempted a task outside its job, would the platform block it? If the answer is no, the governance lives in a prompt, not in a control.
The stealable pattern is a one-page permission map. List the workflow, the systems it touches, the data it can read, the fields it can write, the actions it can trigger, and the conditions that require escalation. This artifact is useful to operations, security, and auditors because everyone can inspect the same boundary.
Rule three: draw the line before the exception
Autonomy is not a binary switch. It is a series of decisions about which actions are routine, reversible, and governed by known rules—and which ones carry judgment, liability, or a costly point of no return. Pallet places document collection, required-field validation, rate retrieval, routine shipment updates, and rule-based reconciliation on the more autonomous side of that line. Financial commitments, customer promises, regulatory exceptions, and irreversible system changes belong closer to a human approval gate.
The time to draw that line is before an agent meets a messy Tuesday afternoon. If escalation depends on the agent improvising when to ask for help, the organization has outsourced governance to the very system it is trying to govern. Approval thresholds should be explicit: a dollar amount, a class of customer commitment, a confidence score, an exception type, or an irreversible action.
This does not make the human a ceremonial rubber stamp. The interface should show the evidence, the proposed action, the relevant rule, and the consequence of approval. Human-in-the-loop only works when the human is put in the loop with enough context to make a better decision than the machine.
The autonomy line
Rule four: keep the receipts
For ordinary generative AI, teams often judge the answer on the screen. That is inadequate for an agent that completes a multi-step workflow across several systems. A plausible final result can hide a bad source, an unauthorized detour, or an incorrect intermediate change. Pallet’s framework asks companies to make every execution transparent and auditable: which agent ran, who initiated it, which systems it accessed, what information changed, and where a person intervened.
The useful unit of evidence is not a transcript dump. It is a structured execution record that can be searched, replayed, and exported into the company’s existing security monitoring. Operations needs it to resolve exceptions; IT needs it to detect misuse; risk teams need it to demonstrate that controls operated as designed.
“Govern the movie, not the screenshot.”A practical rule for agentic operations
The final shipment record is the screenshot. The movie includes the email that started the job, the document the agent parsed, the rate source it queried, the field it changed, the approval it requested, and the final write. When something goes wrong, the movie turns a mystery into an incident that can be understood and fixed.
Rule five: govern the factory, not just the worker
Execution controls answer what an approved agent may do. Lifecycle controls answer who may create, configure, test, publish, modify, and retire that agent. Pallet separates the two because an agent is more than a login. It encodes instructions, permissions, escalation rules, and system connections—the operational process itself.
That means the person allowed to run a quoting agent does not automatically need the power to rewrite its pricing instructions. A reviewer may approve outputs without being able to publish a new version. Administrators can manage credentials and rollout states without owning every business rule. These role-based divisions resemble controls already used across enterprise software, which is precisely the point. Familiarity makes them easier to explain and harder to waive away.
Versioning belongs here too. A company should know which configuration ran each workflow, what changed between releases, who approved the change, and whether the previous version can be restored. If an agent improves every week but its controls cannot say which version acted yesterday, rapid iteration has erased accountability.
The control surface is the product
The five rules form a compact operating model: identity says who; permissions say where; autonomy thresholds say when to stop; execution logs say what happened; lifecycle controls say who can change the rules. Remove any one and the others weaken. A perfect log only documents an over-privileged mistake. A narrow permission set becomes unreliable if anyone can silently republish the agent. A human approval gate is theater if the reviewer cannot see the evidence.
This is why governance should not arrive as a policy document after the demo. It has to live in the product’s control surface and deployment process. The strongest teams can inspect an agent’s scope before launch, simulate its behavior, review exceptions in production, and tighten or expand authority based on evidence. More autonomy becomes something earned, not assumed.
Pallet says its agents are designed for supply-chain operations, where work spans channels such as email, voice, APIs, and remote desktops. The company also emphasizes simulations, adversarial tests, operational knowledge, and enterprise monitoring. Those claims put a useful burden on governance: controls must survive contact with the messy systems and exceptions where real logistics work happens.
The goal is useful authority
There are two easy ways to fail with agentic AI. Give the agent broad access and hope its instructions hold, or make every action wait for approval until the automation becomes a slower inbox. Pallet’s framework points to the harder middle: enough authority to complete meaningful work, bounded tightly enough that exceptions remain visible and recoverable.
That middle will move. A task that begins with mandatory review may earn autonomous status after thousands of clean executions. A new customer rule or regulatory change may push it back behind a gate. Governance is therefore not a launch checklist. It is an operating rhythm built from telemetry, exceptions, access reviews, and version control.
The best proof of governance is not that an agent never makes a mistake. People and software both do. It is that the organization can contain the mistake, explain it, correct the process, and know which other executions were affected. In that sense, the ambition is larger than safety. Good governance makes autonomy usable. It lets operators stop doing every repetitive step while preserving the judgment and accountability that keep physical operations moving.
The five-question preflight
Before an agent runs, ask: Who is it? What can it touch? Where must it stop? Can we reconstruct every action? Who can change or publish it?
The agent may take the wheel. The enterprise still chooses the route, sets the speed limits, and keeps the black box running. Read Pallet’s original governance principles.