At Sterling-Hoffman, a recruiting agency handling sensitive candidate and client information, the first obstacle to a new security tool was another security tool. Recently deployed endpoint protection blocked Harmony Purple’s scanning process. Orchestra Group’s customer case study says the conflict was identified and resolved; deployment then proceeded smoothly. It is a wonderfully unglamorous opening. Before a system can reveal your weaknesses, your existing defenses must let it look.
- Harmony Purple maps attack paths and ranks repairs.
- Harmony IoT watches Wi-Fi, Bluetooth and nearby connected devices.
- Smaller organizations and service providers are the central audience.
- Useful automation still depends on discovery, access and follow-through.
That small collision captures Orchestra’s larger proposition. Security teams have information to spare and time to ration. A vulnerability report can tell them what is wrong without settling what matters most. Orchestra sells a way of connecting those weaknesses to the assets a business wants protected. Its product must earn its place in the machinery already running, then help the people operating that machinery choose their next move.
The flaw is only half the story
Harmony Purple begins with agentless discovery: servers, network equipment, applications, configurations, security controls and vulnerabilities. It builds what Orchestra calls a Digital Cyber Twin, a virtual representation of the IT estate. Attack-path simulation then explores how weaknesses could connect. The company describes its engine as reasoning-based AI, designed to model attackers’ methods rather than merely spot statistical patterns in observed behavior.
The distinction is practical. A severe flaw on an isolated machine and a less conspicuous flaw opening a route to a critical asset need different attention. Orchestra’s argument is that business context should determine the repair order. The output is intended for two audiences: IT staff who must act, and executives who need to understand the risk. A useful report has to survive both conversations.
Its solution guide makes the idea concrete with an illustrative network: 1,010 vulnerabilities on 850 hosts narrow to 590 exploitable vulnerabilities, then 65 attack paths to ten high-value assets. The final recommendation is to patch 15 hosts and close two ports. These are teaching figures, not a customer result. Their purpose is to show how a daunting inventory might become a manageable intervention.
The buyer wanted a view, not another chore
Sterling-Hoffman’s IT manager, Marina Strongin, selected Harmony Purple for coverage, attack-path analysis and ease of use, according to the published case study. The agency wanted low-impact scanning, accurate discovery and guidance on which hosts needed patches. Lower purchase and operating costs were also selection factors. Her team chose the product to understand exploitation in its own infrastructure, rather than simply accumulate a catalogue of open weaknesses.
“clear picture of what is going inside the network”Marina Strongin · Sterling-Hoffman
Orchestra customer case study
Strongin’s description of the result is modest enough to be useful. Once the scanning conflict was resolved, she reported responsive support and a clearer view inside the network. The story offers a copyable buying criterion: evaluate whether the tool explains your environment and helps prioritize work. A persuasive dashboard matters less than the quality of the decisions it supports.
A bank’s missing addresses
Lowell Five Bank supplies a second, different test. In Orchestra’s 2021 case study, its team had already moved from an agent-based system to an agentless alternative. The replacement repeatedly missed IP addresses, leaving staff to find and add them manually. With more than 1,000 IP endpoints spread across locations, subnets and VLANs, avoiding agent maintenance was attractive. Incomplete discovery was an expensive nuisance in staff time.
The bank chose Harmony Purple for reliability, efficiency, report clarity and cost. Thomas D’Entremont, its vice president of network systems, said installation took two or three days. The case study reports more consistent discovery, less emergency patching and better communication with executives and the audit committee. These are customer accounts published by the vendor. They describe operational benefits; they do not establish a universal reduction in breach probability.
The company assembled its instruments
Orchestra was founded in 2018 by Omri Lavie, Jacob Ukelson and Isaac Zack. Lavie and Zack brought entrepreneurial and investment experience; Ukelson’s background includes IBM, Informatica and CA. Its original proposition emphasized coordinating security products that did not work comfortably together. In April 2020, a $7.5 million financing round led by Prytek backed that approach.
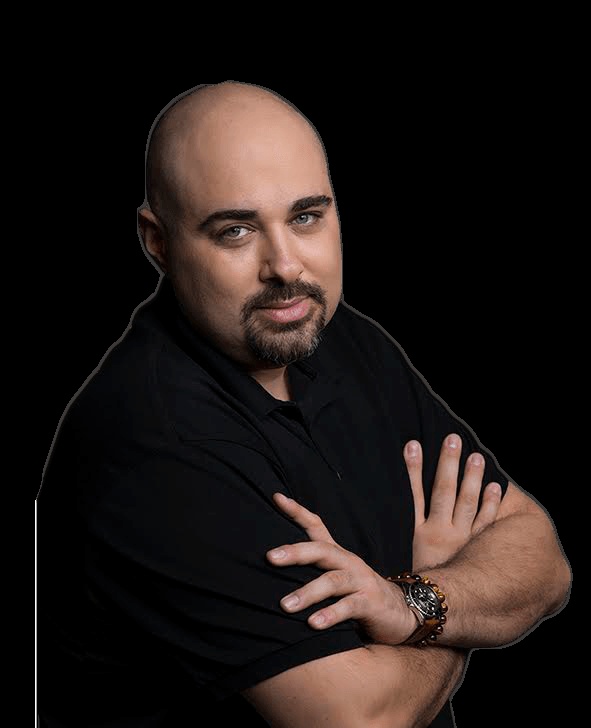 Omri Lavie / CEO
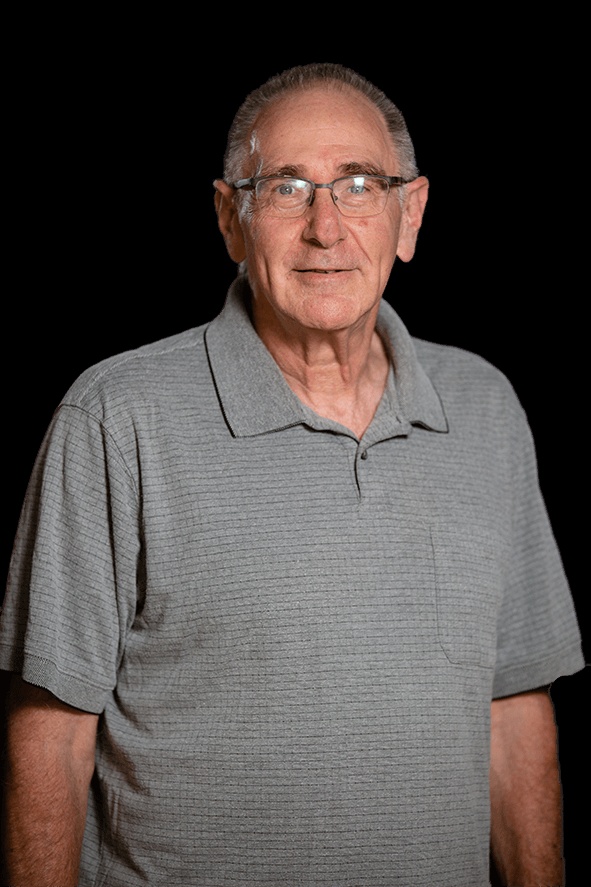 Jacob Ukelson / CTO
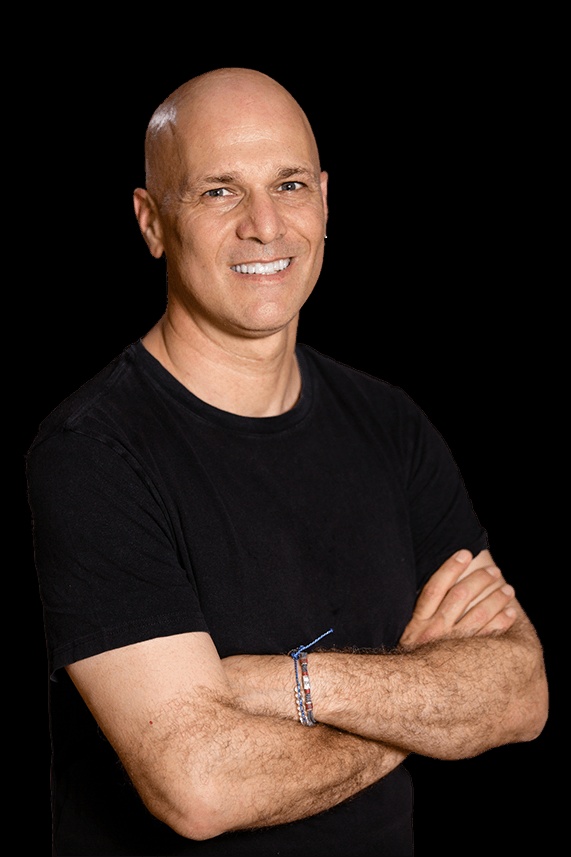 Isaac Zack / COO
Acquisitions supplied additional capabilities. The Cronus purchase, announced in May 2020, added technology described as virtual hackers that identify and prioritize vulnerable attack routes. Netformx followed in December 2021, bringing network discovery and analysis expertise alongside an established IT channel business. These deals help explain Orchestra’s name: the company’s history concerns making separate capabilities perform together, with business risk as the score.
The perimeter has an airspace
Harmony IoT tackles a different blind spot. Wi-Fi and Bluetooth devices operate in and around business premises, including devices outside ordinary network management. Orchestra describes monitoring their activity, comparing expected behavior with known attack behavior, and enforcing wireless policies. Mitigation can include interrupting connections or isolating threats. The useful question becomes who is communicating nearby, with what, and whether that conversation should continue.
The company markets this coverage to financial services, healthcare, manufacturing, retail and hospitality. Its solutions page describes bogus access points that lure hotel guests or employees into handing over credentials. Harmony IoT uses on-site sensors; this is a physical deployment task as well as a software purchase. For buyers, sensor placement and the wireless environment belong in the evaluation, alongside the appeal of seeing previously unmanaged devices.
A repair list still needs a repair crew
Orchestra sells licensed security products directly and through partners and managed service providers. A May 2022 Netpoleon agreement expanded distribution in India and included engineer training. In December 2022, Orchestra announced a CyberArk integration for managing Purple’s scan credentials centrally. Its December 2023 blog connected Purple to continuous threat exposure management, or CTEM: an ongoing program of finding exposures, prioritizing them and checking improvement.
The practical lesson is to test the whole loop. Confirm discovery against your asset inventory. Test compatibility with endpoint protection. Check that scan credentials provide the intended access. Ask who will patch systems or apply compensating controls, then rescan. A model cannot account for an asset it never discovers, and a recommendation cannot fix a system by being admired. Orchestra’s proposition succeeds when the shorter list becomes completed work.