The internet has a front of house and a boiler room. The front is all glassy applications, AI assistants and one-click promises. Downstairs, DNS turns names into destinations, DHCP hands devices their addresses, and IPAM keeps the address book from becoming a junk drawer. Infoblox lives downstairs. Its achievement has been to make that uncelebrated machinery reliable enough for a bank, university, factory or telecom operator - then persuade the security team that the boiler room has the best view of burglars approaching the building.
Founded by Stuart Bailey in Chicago in 1999, Infoblox began with a hardened DNS appliance. The premise was gloriously practical: core network services should not depend on a fragile general-purpose server maintained by heroic administrators and mysterious scripts. In 2005, its SilverBox bundled nonstop DNS and DHCP. The company later acquired iPANTO for IP address management and Netcordia for network configuration automation. Three awkward jobs became one category: DDI - DNS, DHCP and IPAM.
The first failure is usually the map
What breaks first in a sprawling network is often not a router. It is the shared understanding of what exists. A team adds a cloud account, another inherits Microsoft DNS, a third records addresses in a spreadsheet, and an acquisition arrives with its own conventions. Soon, a routine change risks a duplicate address, stale record or outage. Nobody has a complete map, so every ticket begins with archaeology.
One Infoblox case study describes a large financial-services company running about 30 networking products and versions. The customer consolidated DNS, DHCP and IP address management on Infoblox and reported $2 million in annual savings. The sharper quote came from its networking executive: “Infoblox has never once caused us an outage.” It is marketing material, but it captures the actual purchase criterion. Nobody buys DDI to feel inspired. They buy it because a broken lookup can make a perfectly healthy application disappear.
What does the software cost? Infoblox does not post a dollar menu. Its current model sells contract-term pools of tokens, which customers consume across Universal DDI or Threat Defense capabilities. Usage can be tied to services, servers, discovered assets, users and appliance capacity; support, hardware and migration services may sit beside the subscription. The “True Forward” policy lets usage run above entitlement without retroactive penalties, then resets the future level. Flexible, yes. Simple to benchmark, no. A serious buyer should model renewal exposure before admiring the single pane of glass.
DNS became the tripwire
The strategic turn came when Infoblox stopped treating DNS as only an operations service. Malware needs infrastructure too. A phishing kit, command-and-control server or lookalike brand domain must be registered, configured and queried. Those preparations create patterns before an attack reaches its victim. Infoblox acquired threat-intelligence company Internet Identity in 2016; its technology and analysts became building blocks for Threat Defense.
Threat Defense sits in that lookup path. It evaluates requested domains, blocks known or predicted malicious infrastructure, and sends context to the rest of the security stack. The company says its system can protect users and unmanaged devices without an endpoint agent because every cooperating device needs a resolver. It also claims it blocks 90 percent of threats before the first query and detects threats an average of 68 days earlier than other tools. Those are vendor benchmarks, not laws of physics, but the mechanism is sound: find the attacker while the attack site is still being assembled.
There are boundaries. Protective DNS sees traffic that actually passes through the protected resolver. Hard-coded IP addresses, unauthorized encrypted DNS, compromised trusted domains and application-layer behavior may need endpoint, identity, email, firewall and browser controls. Infoblox is not a replacement for the security stack. Its difference is placement: it combines DDI’s authoritative network context with a checkpoint nearly every connection must visit.
The appliance company changed its mind
The old Infoblox sold hardened boxes into data centers. The modern enterprise scattered workloads across AWS, Azure, Google Cloud, branches, remote workers and SaaS. An appliance-only worldview could not keep the map current. After an IPO in 2012, Vista Equity Partners took Infoblox private in 2016 for about $1.6 billion. Warburg Pincus joined Vista as an equal investment partner in 2020, explicitly backing cloud-managed networking and the BloxOne platform.
Universal DDI, launched in 2024, is the clearest result. It offers one cloud control plane and API for on-premises NIOS, Microsoft DNS and DHCP, public-cloud services such as Route 53, Azure DNS and Google Cloud DNS, plus external providers including Cloudflare and Akamai. Customers can modernize management without ripping out every underlying server. By November 2025, Infoblox said the suite had passed 200 customers.
The portfolio still has distinct layers. NIOS DDI remains the sturdy core for organizations that want dedicated physical or virtual infrastructure. NIOS-X can run closer to branches and workloads, including as a service. Universal Asset Insights inventories the estate and surfaces problems such as conflicting addresses or abandoned DNS records. NetMRI watches network-device configuration and compliance. Professional services help with the part vendors rarely place in the diagram: migrating years of records, policies and homegrown processes without interrupting the business. This is why Infoblox competes as much with scripts, spreadsheets and institutional habit as it does with another logo.
The hyperscaler partnerships make the neutral-control-plane argument more credible. Universal DDI integrates with Google Cloud WAN, while Google Cloud DNS Armor uses Infoblox intelligence. AWS customers can buy managed threat rules through the AWS Marketplace. Microsoft environments can retain their existing DNS and DHCP servers while putting management above them. The attraction is not that Infoblox replaces every cloud. It gives a central network team a consistent policy and audit surface when developers quite reasonably refuse to choose only one.
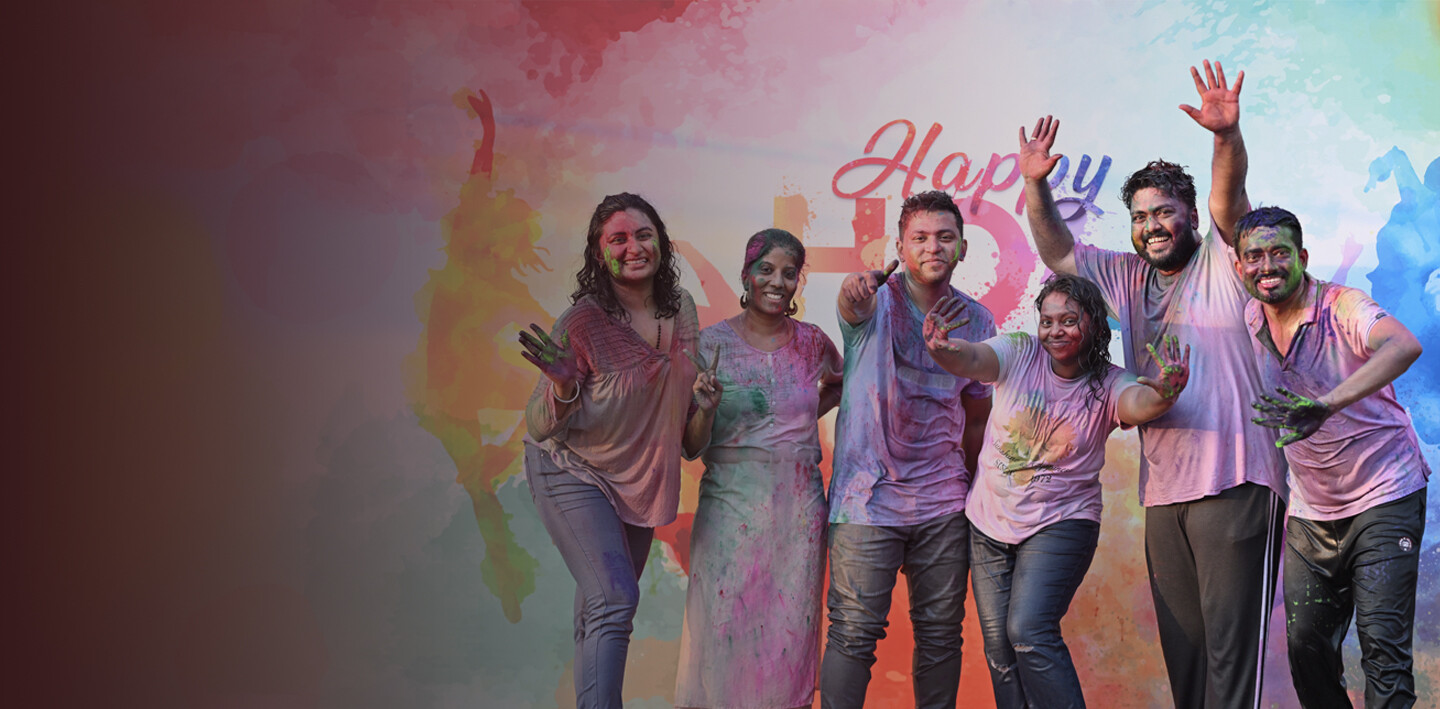
Infoblox employees celebrate Holi. The network diagrams are usually less colorful, although the company does call its staff “Bloxers.”
The culture is more explicit than the product category might suggest. Employees are “Bloxers,” and the published values include integrity, customer obsession, transparency and the wonderfully unvarnished “no jerks.” Infoblox says staff receive hybrid-work options, learning support, employee resource groups and 16 volunteer hours each year. These are company-stated commitments, not a substitute for employee experience, but the plain language suits a business built around reducing ambiguity. Even its culture page sounds like a configuration policy: collaborate, debate respectfully, assume good intent, then act.
In 2026 the borders widened again. The Axur acquisition added external digital-risk protection, including discovery of phishing pages, impersonation and exposed credentials. Kentik added live flow, routing, path and performance telemetry. Infoblox IQ added agentic workflows intended to investigate stale records, configuration drift and suspicious DNS activity. The logic is coherent: DDI knows what infrastructure is supposed to exist; Kentik shows what the network is doing; threat intelligence judges where traffic wants to go; an AI layer helps operators ask questions and act.
Who should buy the whole idea?
Infoblox fits organizations where network truth is both difficult and consequential: global companies, banks, hospitals, universities, public agencies and service providers. Its customer roster includes Adobe, Aflac, Providence, the University of Florida and the City and County of San Francisco. The company says more than 5,700 organizations use its products, including 75 percent of the Fortune 500.
The users are usually not the people approving the invoice. Network engineers want fewer manual changes and a dependable inventory. Cloud teams want APIs and faster provisioning. Security analysts want domain context without another flood of context-free alerts. The chief information officer wants fewer outages; the chief security officer wants earlier warning. Infoblox’s commercial trick is giving those groups a shared substrate while selling subscriptions, token capacity, support and services around it. That also creates organizational friction: consolidation only pays when teams agree on ownership, naming and policy. A new dashboard cannot negotiate that truce for them.
The alternatives depend on the job. BlueCat, EfficientIP and Cygna Labs compete directly in DDI. Cisco and ManageEngine cover parts of the territory. Native cloud DNS and IP tools may be enough for a young company that lives in one cloud. In security, Cisco Umbrella, Cloudflare and larger platform vendors contest protective DNS and adjacent controls. Infoblox’s advantage is depth across DDI and DNS intelligence. Its liability is the same thing: smaller teams may not need the machinery, migration or enterprise contract.
Conditions where it works
Many sites, clouds and inherited DNS systems; strict uptime; enough operational scale to reward automation; a SOC ready to use DNS context.
Conditions where it does not
Simple single-cloud estates; tiny address spaces; no staff to run governance; traffic that bypasses protected DNS; budgets that favor native or open-source tools.
Start with the boring control point
- Choose a system every workflow already touches.
- Make it the reliable source of truth before adding analytics.
- Expose it through APIs so routine work becomes repeatable.
- Turn the resulting context into a second product for an adjacent buyer.
That sequence is the lesson worth stealing. Infoblox did not begin by promising AI transformation. It took custody of a tedious, unavoidable layer, earned trust through uptime, and expanded from operations into security. The current platform push may still stumble on integration, price or the familiar enterprise problem of offering too much. Axur and Kentik were only acquired in 2026, and their deepest product integrations remain ahead. Yet the strategic bet is unusually legible: if you know what every asset is called, where it lives and where it is trying to go, you have a decent chance of spotting trouble before the sirens.